AI readiness checklist for one job at a time

On this page
AI & Automation
You run operations at a company of about sixty people. A vendor demo went well, and leadership wants the supplier-invoice inbox automated next quarter. Your AI readiness checklist should score that single job against MUST, SHOULD and AVOID requirements: any failed MUST stops the project, regardless of the total.
The useful question is whether this job has a repeatable procedure, measurable results and controlled access. A convincing demo answers none of those questions by itself.
How to score one job against the standard
Define the job's start, finish and permitted actions before scoring it. For the openly hypothetical example used here, the job starts when an invoice arrives and finishes when a draft bill is ready for approval; payment approval stays outside its permissions. If the candidate job is still vague, use the first AI use case selection criteria to choose a bounded task.
MUST requirements are pass/fail gates. SHOULD requirements earn points, while AVOID items disqualify the job until removed. These are our house requirements for a company of 10 to 200 people, not a certification scheme or regulatory standard.
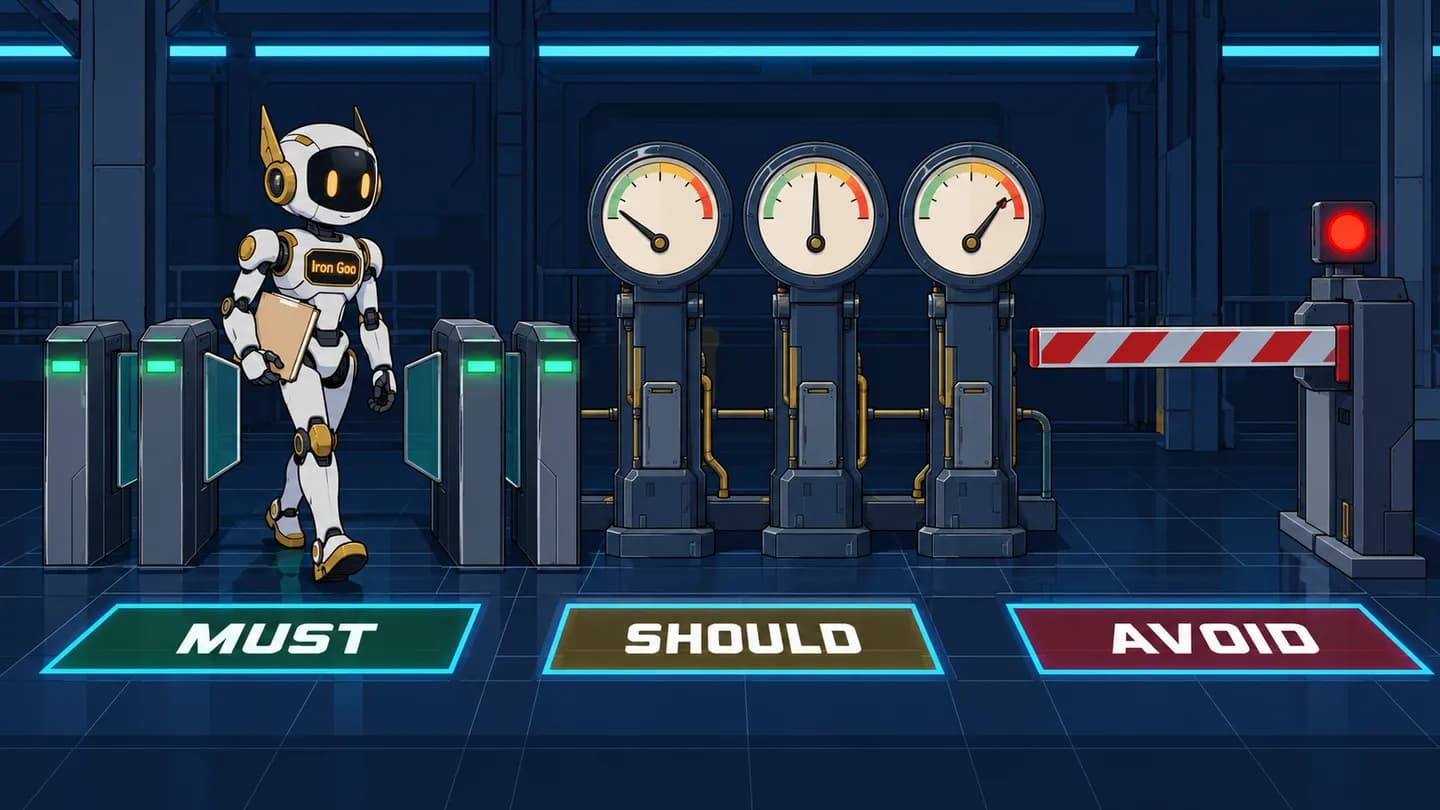
Each folder represents one job. MUST gates must open individually; SHOULD points cannot cancel an AVOID condition.
MUST requirements: eight gates before a pilot
M1. Write a procedure a stranger can follow
Reason. A procedure must specify the normal outcome and what happens when information is missing. For invoice entry, that includes duplicate invoices, missing purchase orders and changed bank details. Our judgment: unresolved human disagreements become unreliable automation instructions.
Test. Give the procedure and five past cases with known outcomes to a colleague who has never done the job. Ask them to complete the cases without help, recording every question. Include an exception case, not five copies of the easiest invoice.
Pass line. Our rule is the correct outcome on at least four of five cases without asking anyone. Every question becomes an edit to the procedure before retesting.
M2. Name an owner who can stop the job
Reason. Someone must decide whether an output is acceptable and whether the automation should continue. Responsibility without authority produces a person who receives alerts but cannot fix their cause. A department name is not an owner.
Test. Hold a short conversation with the proposed owner and their manager. Write down who approves procedure changes, reviews exceptions and can suspend access. Put review time on the owner's calendar and name a backup for absence.
Pass line. One named person has documented authority to pause the job, allocated review time and a backup who accepts the role. “Finance will handle it” fails our gate.
M3. Measure volume, handling time, errors and turnaround
Reason. A baseline makes a later improvement claim checkable. Handling time measures labor; turnaround measures how long the invoice waits between receipt and completed entry. Those numbers can move differently.
Test. Export last month's records with receipt and completion timestamps. Time twenty representative items with a phone stopwatch and use the median handling time; review fifty completed items for errors. Record the monthly volume and median turnaround alongside them.
monthly_labor_cost = items_per_month * minutes_per_item / 60 * loaded_hourly_rate
Assume our hypothetical company handles 600 supplier invoices monthly, with a measured median of six minutes each and a loaded hourly rate of $38. The planning calculation is 600 × 6 ÷ 60 = 60 hours, then 60 × $38 = $2,280 monthly. Multiplying by the median gives a planning estimate; totaling measured handling time would give a more exact labor figure.
Suppose three of the fifty checked invoices had keying errors: 3 ÷ 50 = 6%. Median turnaround is two working days. The $2,280 is the baseline labor estimate, not promised savings: subscription costs and retained human review still need counting.
Time real invoices before changing the workflow. Keep the item identifiers and measurement method so later results can be compared on the same basis.
Pass line. Our gate requires all four numbers, their measurement dates and the spreadsheet used to calculate them. An estimate remembered during a meeting does not pass.
M4. Prove the data is reachable on your current plan
Reason. A visible screen does not establish machine access. API access may require a different subscription, and a person's login creates an ownership problem when that person leaves.
Test. For every system involved, export the required records to CSV or XLSX through its interface. Check the plan comparison or account settings for API access, then identify the company-controlled integration account. Write its permissions as verbs: read invoices, create draft bills, update draft descriptions, never approve payments or send supplier emails.
Pass line. Our gate requires a usable export, API entitlement on the purchased plan, a non-personal integration identity and a written permission list. Record the account and plan evidence; a vendor's general claim that it “has integrations” is insufficient.
M5. Check fifty records for defects in the fields used
Reason. In a July 2024 survey of 1,203 data management leaders, Gartner found that 63% of organizations lacked or were unsure whether they had the right data management practices for AI. Gartner also forecasts that through 2026, organizations will abandon 60% of AI projects unsupported by AI-ready data; this is a prediction, not an observed failure rate. Its requirement that AI-ready data represent the specific use case, including errors and outliers, supports checking the fields this job actually consumes. Cleaning unrelated marketing records will not repair missing supplier identifiers.
Test. Add =RAND() beside exported records, freeze the values and sort to select fifty. Check required fields, duplicates, stale values and formats; use COUNTIF on normalized supplier names to flag possible duplicates for inspection. Check dates, currencies and VAT identifiers against the job's requirements, counting each defective record once.
Pass line. Our house threshold is under 5% defective records in the fields used. From 5% through 15%, fix and rescore; above 15%, treat cleanup as a preceding project, using the data preparation checklist. Each record changes this sample's result by two percentage points, so treat 4% and 6% as effectively the same warning, not a statistically meaningful boundary.
M6. Enforce MFA across every account reaching the data
Reason. A Microsoft study by Meyer and colleagues found that MFA reduced account-compromise risk by 99.22% across the population studied and by 98.56% for accounts whose credentials had leaked. Microsoft Entra security defaults are free and block legacy authentication, including legacy connections through IMAP, SMTP, POP3 and old Office clients. Legacy authentication cannot perform MFA, giving attackers a route around it. Include human accounts controlling integration credentials in your checks.
Test. Open Microsoft Entra sign-in and MFA registration reports, or Google Workspace's 2-Step Verification enrollment report. Compare them with the list of people who can access the mailbox, accounting system and vendor console. Check enforcement as well as enrollment; in Microsoft environments, check that legacy authentication is blocked.
Pass line. Our gate requires 100% MFA enrollment and enforcement for human accounts with access, including administrators. Noninteractive service identities need controlled credentials and scoped permissions; do not invent an MFA enrollment requirement for an identity that cannot interactively sign in.
M7. Read product-specific terms and execute the applicable DPA
Reason. A vendor name does not identify the terms governing a particular product. Training, retention, human review and residency are separate promises. Where the vendor processes personal data for you, record the applicable data processing agreement, or DPA, alongside the order.
Test. Match the actual account and billing tier to the vendor sheet. Save the governing terms, applicable DPA and acceptance or signature record in a shared folder. Fill every unknown with a question for the vendor; silence in a document is not a favorable answer.
Vendor terms are a dated snapshot read on 24 October 2026. “Not stated” means the page read does not say; ask the vendor.
| Product tier | Training default | Prompt/output retention | Human review | Residency | How the DPA is obtained |
|---|---|---|---|---|---|
| OpenAI API | No, unless explicitly opted in | Abuse logs up to 30 days, with exceptions; Responses objects stored for at least 30 days by default when store is true; assistants, threads and vector-store objects kept until deleted, then deleted from servers 30 days later; files kept until deleted | Authorized employees may access stored data for engineering support, investigating potential platform abuse and legal compliance; specialized third-party contractors under confidentiality and security obligations may access it only for abuse and misuse review | EU regional storage and processing at eu.api.openai.com require Zero Data Retention, Modified Abuse Monitoring or another approved retention arrangement | Request through OpenAI's DPA form |
| ChatGPT Business | No training by default | Admin-controlled; deleted or unsaved conversations removed within 30 days, with exceptions | Authorized employees may access stored data for engineering support, investigating potential platform abuse and legal compliance; specialized third-party contractors under confidentiality and security obligations may access it only for abuse and misuse review; workspace admins can also view and export member conversations | Not stated | Request through OpenAI's DPA form |
| Anthropic API and Claude for Work | No training by default; submitted feedback is an exception | API inputs and outputs deleted on the backend within 30 days, with exceptions; Work and Enterprise chats and coding sessions kept in the product until user deletion, with deleted chats removed from the backend within 30 days; feedback kept five years; policy-flagged inputs and outputs up to two years; classification scores up to seven years | For organizations with zero data retention (ZDR) using covered models (Mythos-class models and models Anthropic designates as similar), no personnel can read retained conversations by default; review only through a controlled access path such as an automated trust and safety flag, by a small set of approved reviewers, with every access recorded in a tamper-proof log; human review for a default (non-ZDR) team is not stated | Not stated | Obtain Anthropic's commercial DPA and retain its applicability record |
| Claude consumer plans | User choice | Training opt-in extends applicable chat retention to five years; otherwise the stated 30-day retention continues | Not stated | Not stated | Not stated; fails our company-data rule |
| Gemini API unpaid | Content used for product and model improvement | Google Search grounding content retained 30 days under the Gemini API terms; general duration not stated | Human reviewers may read, annotate and process input and output | Not stated | Not stated; fails our company-data rule |
| Gemini API paid | Prompts and responses not used to improve products | Limited-period abuse logging, duration unspecified; Search and Maps grounding content retained 30 days | Not stated; prompts logged for a limited period only to detect policy violations | Not stated | Verify applicable terms and Cloud DPA coverage |
| Gemini in qualifying Workspace editions | No training without permission or instruction | Admin settings from 90 days to indefinite; Gemini app up to 36 months | Content is not human reviewed for model training outside your domain without permission | Not stated | Covered through the Cloud Data Processing Addendum |
| Gemini Enterprise Agent Platform (formerly Vertex AI) | No training or fine-tuning without permission or instruction | Default cache up to 24 hours; Search grounding logs up to three days; Maps grounding 30 days; Deep Research session data seven days | Not stated | Regional or multi-regional endpoints keep durable cached data in the selected location; the global endpoint can serve requests and cached data from any region | Obtain the applicable Cloud Data Processing Addendum |
The OpenAI API data controls distinguish abuse logs from persistent application objects, including their deletion timelines. Zero Data Retention requires approval and additional requirements; it is not a self-service switch. OpenAI's enterprise privacy page provides the Business and API DPA request route.
Anthropic's commercial training policy excludes training by default, with a feedback exception. Its retention policy lists API exceptions for the Files API and other services with longer retention under your control, a zero data retention agreement, Usage Policy enforcement and legal compliance. Its covered-models retention page, effective 9 June 2026, applies to organizations with zero data retention (ZDR) using covered models (Mythos-class models and models Anthropic designates as similar): for those organizations, no personnel can read retained conversations by default; review occurs only through a controlled access path such as an automated trust and safety flag, by a small set of approved reviewers, with every access recorded in a tamper-proof log; human review for a default (non-ZDR) team is not stated.
The Gemini API terms prohibit submitting sensitive, confidential or personal information to Unpaid Services and state the 30-day retention for Google Search grounding. User-facing API clients in the EEA, Switzerland or UK must use Paid Services, and regional paid data-use treatment does not establish storage residency.
The Workspace privacy hub describes its separate organizational controls. The Gemini Enterprise Agent Platform (formerly Vertex AI) zero data retention steps require keeping request-response logging off, setting store to false on the Interactions API, keeping Live API session resumption off, turning off caching, avoiding Google Search and Google Maps grounding, and avoiding the Sandbox Snapshot API. Search grounding logs persist up to three days, Maps grounding data 30 days and Deep Research session data seven days; those retention periods cannot be disabled for those features.
A training exclusion does not promise immediate deletion or exclude every review. Check persistent files, abuse logs and legal exceptions separately before approving the product tier.
Pass line. Our gate requires an approved product tier, resolved handling questions and an executed or otherwise binding applicable DPA for processor relationships involving personal data. Keep its date and storage location in the job record; if no personal data is involved, document that determination.
M8. Restrict permissions and drill the kill switch
Reason. Reading an invoice and approving its payment carry different consequences. A permissions list only becomes credible when an administrator demonstrates that the job can be stopped.
Test. Compare the integration account's actual permissions with M4's verbs. In a controlled drill, revoke its access from the designated control point and attempt one harmless read or draft action. Start a stopwatch before opening the control.
Pass line. Our threshold is revocation from one place in under five minutes, with the attempted action demonstrably blocked. An on-screen pause indicator alone fails; retain the drill time and result.
SHOULD requirements: five controls worth scoring
S1. Centralize offboarding through SSO where available
Reason. Single sign-on connects application access to the company identity lifecycle, although existing sessions and separate API credentials still need checking. Some vendors reserve SSO for expensive plans: the SSO tax is a purchasing constraint worth discovering before commitment.
Test. List which connected applications support SSO on your plan. Pick the last employee who left and verify that their access is gone everywhere this job touches. Microsoft Entra security defaults provide a free floor for MFA and legacy-authentication blocking; Conditional Access requires at least Entra ID P1.
Pass line. Our full-score threshold is configured SSO where available plus a successful offboarding check. Award partial credit for a documented, tested manual removal checklist while pricing the missing connections.
S2. Publish an AI use policy that addresses shadow AI
Reason. An approved integration does not stop employees pasting the same invoice into personal chat accounts. A useful policy names approved products and forbidden data, then explains how people request exceptions.
Test. Give staff a one-page policy and ask which account they would use for a supplier invoice containing personal information. Check that it covers feedback buttons, uploads and reporting accidental disclosure. Use the AI governance and risk framework when this needs a wider organizational program.
Pass line. Our full-score threshold is a published policy with named approved tiers, data restrictions and a reporting route, plus staff able to apply it to the invoice example. A draft earns partial credit.
S3. Record the legal classification of each automation
Reason. Company size does not settle legal duties; the use and affected people do. Confirm your role and obligations with counsel, because this is general information. Invoice extraction usually has a different AI Act classification from recruitment screening or creditworthiness scoring.
Test. Create one register row with these fields: job, personal-data categories, legal basis, processor and DPA, international transfer mechanism, AI Act role and class, notices, human decision point and log retention. For our invoice example, inspect supplier contact details and bank information, then trace where each field goes.
The AI Act can reach EU deployers and organizations outside the EU when system outputs are used in the EU. Under Regulation (EU) 2026/1744, which entered into force on 27 July 2026, the high-risk application dates moved. Use the amended calendar when recording obligations.
- 2 February 2025Prohibitions and AI literacy apply
Prohibited-practice rules and the original Article 4 literacy duty began applying. Article 4's wording was subsequently amended.
- 2 August 2025General-purpose model obligations begin
GPAI model obligations and governance provisions began applying. These are distinct from a deployer's high-risk duties.
- 2 August 2026General application and transparency
The Act generally became applicable, subject to exceptions. Article 50 transparency rules began applying.
- 2 December 2026Specific marking deadline and new prohibition
Providers of generative systems already on the market reach the Article 50(2) machine-readable marking deadline. The new prohibition concerning non-consensual sexual content and CSAM generation also applies.
- 2 December 2027Annex III high-risk requirements apply
The amended date covers high-risk use cases such as employment screening and creditworthiness scoring.
- 2 August 2028Regulated-product high-risk requirements apply
The amended date applies to high-risk systems embedded in regulated products covered by Annex I.
Amended Article 4 requires providers and deployers to take measures supporting staff AI literacy development. It expressly does not require guaranteeing a specific individual's literacy level. Record job-specific instruction on limitations, escalation and safe handling, with attendance evidence.
Article 50(1) places direct-interaction disclosure duties on providers unless the AI interaction is obvious. Say you put your own API-based customer chatbot into service under your name. Our reading is that you are likely its provider; have counsel confirm. Article 50 also addresses deepfake disclosure, informing people exposed to emotion recognition or biometric categorization, and public-interest text, subject to its human-review or editorial-control exception.
For high-risk systems, Article 26 requires use according to instructions and competent, authorized human oversight. It also covers relevant and sufficiently representative input data under your control, monitoring, serious-incident reporting and controlled logs retained for at least six months. Workplace deployment requires informing workers' representatives and affected workers; Annex III decision systems also require informing affected people.
Under the GDPR official text, Article 28 governs processor contracts. Article 30's exemption for organizations below 250 employees has exceptions, including non-occasional processing, so regular customer-data processing commonly needs records. Article 35 concerns high-risk processing impact assessments; Article 22 addresses solely automated decisions with legal or similarly significant effects.
Article 33 requires notifying the supervisory authority of a personal-data breach within seventy-two hours where feasible, subject to its risk exception. Put the incident contact and escalation route in the register. A DPA does not decide whether the underlying processing is lawful.
Under the official English KVKK text, Article 9 governs transfers abroad, including sending personal data to a US-hosted API. Where you use the Board's standard-contract safeguard, the controller or processor must notify the Authority within five business days after signature. Article 12 requires technical and organizational security measures and addresses responsibility alongside processors; the Turkish text prevails.
Do not assume a small workforce establishes a VERBİS exemption. Reported changes affect special-category-data businesses and businesses without balance-sheet-basis books. Check the Authority's current criteria against your activity and finances, recording the answer separately from the transfer mechanism.
Pass line. Our full-score threshold is a completed row with applicable duties, evidence and responsible people identified. A partially completed row earns partial credit; unresolved legality or transfer safeguards block real-data use regardless of SHOULD points.
S4. Define a shadow run and acceptance threshold
Reason. Shadow mode lets you compare proposed actions with actual decisions while keeping the automation from executing them. Draft accuracy alone misses the cost of reviewing every draft.
Test. Write the pilot acceptance sheet in an afternoon. Our proposed threshold for the invoice example is fifty representative cases, zero unauthorized actions, no more than the baseline three keying errors, median review time below six minutes and no worse turnaround. Include exception cases and an owner for every disagreement.
Pass line. Award full credit when the threshold, comparison method and review responsibilities are approved and the action path demonstrably cannot execute. Award partial credit for a draft plan; passing this readiness item authorizes the shadow test, not live operation.
S5. Keep a manual fallback someone can run
Reason. Suspending access is useful only if invoices can still be processed. A fallback needs a queue and a reconciliation method so restarting does not create duplicate bills.
Test. Ask the backup owner to identify the last confirmed item, list pending invoices and process a historical case manually. Then have them explain how they would mark work completed during the outage before restarting automation.
Pass line. Our full-score threshold is a written fallback successfully rehearsed by the backup. An untested document earns partial credit; memory earns none.
AVOID requirements: five conditions that disqualify the job
A1. Use consumer or free tiers for company data
Reason. Our rule excludes consumer and free AI tiers from handling company or personal data. Their product terms and administrative controls can differ materially from commercial offerings, even when the interface looks familiar.
Test. Compare the account's product name and invoice with M7's sheet. Ask staff to demonstrate which account receives uploads; use a fabricated invoice for the demonstration.
Pass line. No company or personal data enters an excluded tier. Synthetic demonstrations do not establish approval for real records.
A2. Run the job on an employee's personal login or key
Reason. Personal credentials tie business continuity to an individual's account and departure. A shared password does not turn that account into a company-controlled integration identity.
Test. Open the integration settings and identify the credential owner, recovery contact and revocation control. Compare them with the company account register.
Pass line. The job uses documented company-controlled credentials with a named administrator and tested revocation. Remove personal credentials before rescoring.
A3. Average readiness across the company
Reason. A strong sales workflow cannot compensate for an uncontrolled payment permission. An organizational average conceals the exact failure the project must fix.
Test. Put one job name at the top of the score sheet. Check that every evidence link concerns that job and that no failed MUST has been converted into points.
Pass line. One sheet scores one bounded job, with eight separate gate results. Company-wide percentages cannot authorize its pilot.
A4. Treat a training exclusion as a deletion guarantee
Reason. Training restrictions leave separate questions about retained files and enforcement logs. A purchase decision based on one promise can silently assume three others.
Test. Ask the owner to locate the retention duration, review conditions and residency arrangement independently of the training statement. Mark unspecified answers explicitly.
Pass line. All four promises have separate entries and accepted limitations. An unsupported “the vendor keeps nothing” statement disqualifies the assessment.
A5. Automate an unmeasured or weekly-changing procedure
Reason. A moving procedure prevents a fair comparison and makes yesterday's instructions unreliable. Missing measurements also prevent checking whether review effort consumes the expected savings.
Test. Compare recent procedure versions and ask the owner which decision rules changed each week. Verify M3's dated baseline against the current version.
Pass line. The procedure is stable enough to document and test, with current measurements. If its rules change weekly or the baseline is absent, choose another job.
Score the job and make the decision
Use P or F for each MUST. For SHOULD items, our scoring is 0 for absent, 1 for partial or untested and 2 for meeting the stated pass line. Mark each AVOID item clear or present.
| ID | Requirement | Type | How scored | Your score |
|---|---|---|---|---|
| M1 | Stranger can follow procedure | MUST | P/F | |
| M2 | Authorized owner with time | MUST | P/F | |
| M3 | Four baseline measurements | MUST | P/F | |
| M4 | Machine access and integration identity | MUST | P/F | |
| M5 | Fifty-record quality check | MUST | P/F | |
| M6 | MFA coverage and enforcement | MUST | P/F | |
| M7 | Approved terms and applicable DPA | MUST | P/F | |
| M8 | Scoped permissions and kill-switch drill | MUST | P/F | |
| S1 | SSO and verified offboarding | SHOULD | 0/1/2 | |
| S2 | Published AI use policy | SHOULD | 0/1/2 | |
| S3 | Compliance register row | SHOULD | 0/1/2 | |
| S4 | Shadow acceptance plan | SHOULD | 0/1/2 | |
| S5 | Rehearsed manual fallback | SHOULD | 0/1/2 | |
| A1 | Consumer or free tier handling company data | AVOID | Clear/present | |
| A2 | Personal login or key | AVOID | Clear/present | |
| A3 | Company-wide average authorizes job | AVOID | Clear/present | |
| A4 | Training confused with retention | AVOID | Clear/present | |
| A5 | Missing baseline or weekly-changing rules | AVOID | Clear/present |
If you want an outside assessment after scoring, the operations audit and automation service assesses each task as agent-suitable or not and can build the scoped credentials and human-verified shadow run. Bring the evidence sheet so the review starts with observable gaps.
Apply our decision rule: any present AVOID stops the project until removed, and unresolved legal requirements prevent real-data use. With all eight MUSTs passing and at least six of ten SHOULD points, our 60% threshold, start the shadow pilot under S4's acceptance plan.
If exactly one MUST fails, fix that gate and rescore in two weeks, our review interval. If two or more fail, pick a different job; if every MUST passes but SHOULD points remain below six, complete the missing controls before the shadow run.

Put your next steps in order
Build on what you have just read with a free ebook on semantic SEO and AI visibility. Get worked examples, decision rules, checklists and a do-this-week action in every chapter, plus a six-week plan for your site.