AI Governance for Small Business

On this page
- What does AI governance actually mean at our size?
- What must an AI acceptable-use policy cover?
- How much shadow AI is there, and is banning it the answer?
- How do we find the AI tools people already use?
- Which data can employees put into ChatGPT or another AI tool?
- What should we ask an AI vendor before signing?
- What is the NIST AI RMF, and what should a small company take from it?
- What is ISO/IEC 42001, and do we need certification?
- What does the EU AI Act require of us, and when?
- Who owns what the AI produces?
- Are we covered if AI output infringes someone's copyright?
- What do we do when something goes wrong?
- Does our insurance cover AI mistakes?
- What is the order of work for the first month?
AI & Automation
AI governance for a small business is five written things with one named owner: an acceptable-use policy, an inventory of AI tools and automations, a data-to-tool rule, a vendor sheet with terms read and dated, and an incident runbook. Frameworks and laws determine what belongs in those records. For a company of 10 to 200 people, the useful starting point is someone authorized to approve a tool, stop an automation and require a human check.
What does AI governance actually mean at our size?
It means maintaining those five records and giving one named person authority to say no. An operations director or IT lead can own them, provided the owner can enforce decisions about accounts, purchasing and deployment.
The inventory records each tool and tier, its owner, purpose, permitted data class, users, DPA date, retention number, whether output leaves the company, required human check, applicable AI Act category and review date. Give every automation its own row: a chatbot subscription and a workflow that sends customer emails create different exposures.
The policy tells staff what they may do; the inventory records what actually happens. The vendor sheet supplies evidence for approvals, while the runbook assigns action when a control fails. Store these somewhere staff can find without asking the person who wrote them.
Legal material here is general information. Confirm your role and obligations with counsel, particularly when AI affects employment, credit or people in another jurisdiction.
The trap. A committee can advise the owner, but shared responsibility often leaves nobody able to suspend a tool. A framework becomes useful when it identifies a missing control in these records.
What must an AI acceptable-use policy cover?
Our rule is that an employee AI policy must answer eight questions in writing, including which exact subscription tiers are approved. It must also state that personal accounts and personal API keys are never used for company data.
Use these eight questions as our policy checklist:
- Which tools are approved? Name the product, plan tier and required company account.
- Which data may enter each tool? Attach the data-class table and identify who classifies uncertain material.
- What must never be pasted? Include credentials, API keys, special category data and other people's confidential material under NDA.
- Which outputs require a named human check? Include customer communications, published material, pricing, contractual content and anything about a person.
- When must people be told they are dealing with AI? Specify chatbot disclosure and any applicable Article 50 duties.
- How does someone request a tool? Name the decision-maker; our turnaround rule is five working days.
- How does someone report a mistake or leak? Give one reporting route, with no blame for prompt reporting.
- Who owns the policy, and when is it reviewed? Our rule is every six months and whenever a new tool is introduced.
Apply the policy to contractors using company information as well as employees. Make approval conditional on the tier: permission to use a company business workspace does not approve someone's personal paid account.
Our opinion: two pages that staff can recite beat twenty pages they cannot apply. Include an observable example, such as a customer email that must be redacted before use, so employees can demonstrate the rule during the briefing.
How much shadow AI is there, and is banning it the answer?
Shadow AI is AI used for company work outside the company's approval and oversight. In Microsoft and LinkedIn's 2024 survey, 78% of AI users brought their own tools to work, rising to 80% at small and medium-sized companies.
The Work Trend Index published on 8 May 2024 surveyed 31,000 knowledge workers across 31 markets and found that 75% used AI at work. These are 2024 survey results, not a measurement of your workforce.
Baker Donelson's summary of IBM's Cost of a Data Breach 2026 report reports shadow AI incidents at 43%, up from 20%. The study covered 602 breaches; the summary reports costs of $5.39 million versus $4.63 million. In our reading, the 43% is a share of the breached organizations studied, not of all companies, and the summary does not say what the $4.63 million comparison covers.
Press reports describe Samsung banning generative AI on company devices and networks in 2023 after employees uploaded internal source code. That is a documented reaction, not evidence that bans eliminate use.
Our view is that an approved tool with usable data rules is more likely to work than a blanket ban. A ban may move activity onto personal phones, where your administrator sees even less.
How do we find the AI tools people already use?
Start in Google Workspace's API controls and Microsoft Entra's Enterprise apps, then reconcile the results with spending and a staff survey. These checks reveal connected applications; they cannot reveal every browser session or personal-device conversation.
In Google Workspace, open Security > Access and data control > API controls > Manage App Access > Accessed apps > View list and download the CSV. Sort by user count, inspect requested services and mark AI assistants, meeting note-takers and other tools processing company information.
Google's documented default for unconfigured apps is Allow users to access any third-party apps. The Workspace app-access documentation also notes that details can take 24 to 48 hours to appear after authorization.
In Entra, review enterprise applications and their permission grants. Then open Identity > Applications > Enterprise apps > Consent and permissions > User consent settings; Microsoft's default permits user consent for permissions that do not require administrator consent, including access to the user's own mailbox.
Microsoft recommends limiting user consent to apps from verified publishers and documents an admin consent workflow so employees can request approval. Our advice: configure that workflow and review requested permissions even when the publisher is verified.
Changing consent settings does not revoke grants that already exist. Review and revoke unwanted grants separately; Microsoft's user consent documentation explicitly distinguishes future consent from existing permissions.
Mark AI tools on the exported list, then inspect the permissions behind each entry. An app name alone does not tell you which company information it can read.
Finish the afternoon with card statements, expense claims and one amnesty question: “Which AI tools do you use for work?” Ask for the account type and task, without demanding conversation contents.
Which data can employees put into ChatGPT or another AI tool?
Our rule permits Public material in any approved tool, while Internal and Confidential material require stronger contractual and account controls. Restricted material stays out of general AI tools.
These four classes and their mappings are our rules, not vendor categories or statutory classifications:
| Data class | Examples | Permitted tool tier and conditions |
|---|---|---|
| Public | Published website copy, public documentation | Any approved tool, including a free tier |
| Internal | Procedures, drafts, non-personal business data | Company-account business or enterprise tier, or API, with no-training terms and a DPA |
| Confidential | Customer personal data, contracts, financials, HR records, NDA material | Signed DPA, no training, known retention, company-managed accounts and an inventory row; minimize and redact first |
| Restricted | Passwords, API keys, health or special category data, card numbers, contractually prohibited transfers | No general AI tool; only a separately reviewed, purpose-built automation where permitted, or no AI processing |
The never-paste list still applies within an approved tier. A Confidential classification does not override an NDA or authorize uploading an entire HR folder.
Vendor differences justify the separation. Gemini API unpaid services permit human review and warn against submitting sensitive, confidential or personal information; Anthropic consumer plans can retain data for up to five years when users opt into training.
OpenAI and Anthropic business products generally provide no training by default, but retention depends on the product. OpenAI API abuse-monitoring logs can remain for up to 30 days; Anthropic states backend deletion within 30 days for Anthropic API users, with longer exceptions such as flagged content.
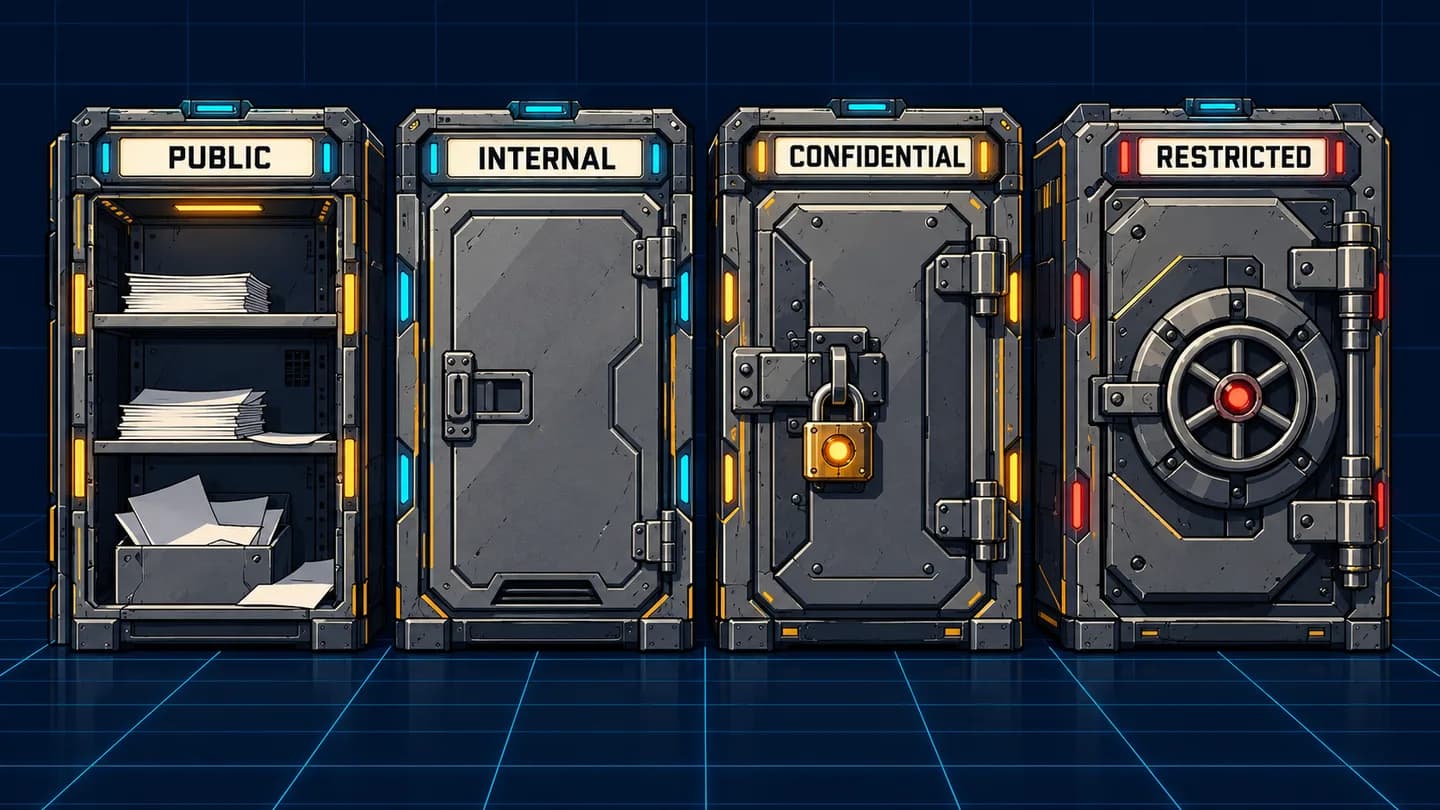
Each class adds conditions before information may enter a tool. Restricted data requires a separate processing decision even when the company already pays for an enterprise plan.
Use the vendor retention sheet and per-job readiness standard to check the exact product tier. A paid consumer subscription is still a consumer subscription.
What should we ask an AI vendor before signing?
Our rule is to complete a 12-question vendor sheet for the exact tier you intend to buy. Accept dated documents and contractual commitments, with numerical answers for retention and notification.
Vendor terms discussed here are a snapshot read on 24 October 2026. Read the agreement that applies to your purchase, including negotiated amendments.
| Question | What a good answer looks like |
|---|---|
| Does our tier train on our content by default? | Explicit no-training language and any exceptions |
| How long are prompts, outputs, files and logs retained? | Separate numbers, deletion timing and exception periods |
| Can humans review our content? | Who, for which purposes and under which access controls |
| Where is data processed and stored? | Available regions, processing exceptions and residency price |
| Is a DPA available and executed? | Signed version, date and stored copy |
| Which sub-processors are used? | Maintained list and contractual change-notice procedure |
| What certifications cover this service? | Scope and date; relevant SOC 2 Type 2 report or ISO evidence |
| Does our tier include SSO, MFA and admin audit logs? | Feature availability, export options and extra charges |
| When will we be told about a breach? | Notification commitment in hours in the DPA |
| What notice precedes model retirement or replacement? | Notice period, channel and migration arrangements |
| Does our tier receive output indemnity? | Applicable clause, exclusions and claim procedure |
| How do we exit? | Export format, deletion confirmation and completion period |
OpenAI's Services Agreement section 5.2 provides audit reports on written request, no more than once a year. Section 14.2 generally caps liability at fees paid during the preceding 12 months, with indemnification obligations carved out.
The trap. An impressive certification does not answer retention, and a DPA does not promise unlimited recovery. Record each answer separately so a missing term stays visible.
What is the NIST AI RMF, and what should a small company take from it?
The NIST AI Risk Management Framework is a voluntary framework released on 26 January 2023, organized around GOVERN, MAP, MEASURE and MANAGE. It has 19 categories and, by our count of its IDs, 72 subcategories; GOVERN applies across the other functions.
NIST itself recognizes that small to medium-sized organizations face different implementation challenges. Our recommendation is to use the functions to check your controls:
- GOVERN: the policy, named owner and vendor approval rules.
- MAP: an inventory row describing purpose, data and affected people.
- MEASURE: a fixed test set per automation and a monthly spot check.
- MANAGE: the runbook, monitoring and a decision to repair, replace or retire a system.
The Generative AI Profile, NIST AI 600-1, released on 26 July 2024, contains about 212 suggested actions by our count. Its 12 risk areas are CBRN information or capabilities; confabulation; dangerous, violent or hateful content; data privacy; environmental impacts; harmful bias or homogenization; human-AI configuration; information integrity; information security; intellectual property; obscene, degrading or abusive content; and value chain and component integration.
Take two action IDs immediately: GV-1.6-001 calls for an inventory of organizational generative AI systems, and GV-4.3-002 supplies incident-record fields. Our judgment is that a small internal-use company should start there, without attempting all 72 subcategories.
What is ISO/IEC 42001, and do we need certification?
ISO/IEC 42001 is an AI management system standard whose first edition was published in December 2023 by ISO/IEC JTC 1/SC 42. It applies to organizations that provide or use AI, and independent certification bodies can audit against it.
ISO/IEC 42006:2025 sets requirements for those certification bodies. Certification involves a maintained management system, including internal audits, management review and surveillance audits, so it creates continuing work and cost.
Our opinion: certification becomes a practical priority when you sell AI products or services to buyers who require it during procurement. For internal use, first ask vendors for evidence covering the services you buy.
Anthropic announced ISO/IEC 42001 certification on 13 January 2025, and Google lists it for Workspace. Record the certificate's scope and date; a vendor's certification does not certify your implementation.
The trap. Buying the standard or attending training does not make the company certified. Ask what procurement problem certification would solve before funding the audit program.
What does the EU AI Act require of us, and when?
Under Article 3(4), a deployer uses an AI system under its authority outside personal, non-professional activity. Small companies have no blanket exemption, and Article 4 literacy measures and Article 5 prohibitions already apply.
The dates in Article 113 reflect Regulation (EU) 2026/1744, which entered into force on 27 July 2026:
- 2 February 2025: initial prohibitions and Article 4 literacy.
- 2 August 2025: general-purpose model provisions.
- 2 August 2026: general application, including Article 50 transparency.
- 2 December 2026: two new prohibitions concerning non-consensual intimate imagery and child sexual abuse material; the Article 50(2) marking deadline for generative systems marketed before 2 August 2026 is a provider duty.
- 2 December 2027: Annex III high-risk requirements.
- 2 August 2028: Annex I high-risk requirements.
Amended Article 4 requires measures supporting staff literacy, without guaranteeing an individual attainment level. The Commission's Q&A says no certificate is needed and an internal training record can be kept; ChatGPT users should understand hallucination risks.
Article 5 already prohibits workplace emotion inference except for medical or safety reasons. Article 50 includes disclosure duties for direct AI interaction, deepfakes and certain public-interest text; the applicable duty depends on your role and use.
From 2 December 2027, Article 26 will require competent, authorized human oversight, monitoring and logs under your control for at least six months for Annex III systems. Employers must inform affected workers and representatives before workplace use, and people subject to relevant decisions must be informed.
Article 25 can make you the provider when you change a general system's intended purpose into a high-risk use, such as ranking job applicants. Article 27 will require fundamental rights impact assessments for specified deployers, including credit-scoring and life or health insurance pricing uses.
Article 99 sets maxima of EUR 35 million or 7% for prohibited practices, EUR 15 million or 3% for specified other obligations, and EUR 7.5 million or 1% for incorrect information. Generally the higher amount applies; for SMEs, including start-ups, each cap uses the lower amount.
SME turnover = EUR 8,000,000 Percentage amount = 8,000,000 × 0.03 = EUR 240,000 SME maximum = min(15,000,000, 240,000) = EUR 240,000
Large-company turnover = EUR 2,000,000,000 Percentage amount = 2,000,000,000 × 0.03 = EUR 60,000,000 Large-company maximum = max(15,000,000, 60,000,000) = EUR 60,000,000
These are maxima under national penalty rules, not expected fines. Scope can reach non-EU companies whose output is used in the EU; for your classification and duties, check with counsel.
Who owns what the AI produces?
Vendor contracts can assign their rights to you, but they cannot create copyright where the law recognizes none. OpenAI says the customer “owns all Output,” then assigns rights “if any”; Anthropic also assigns its interest “if any.”
Google says it “does not assert any ownership rights” in new intellectual property in generated output. Those clauses allocate rights between the parties, without establishing that a generated asset qualifies for protection.
Copyright does not extend to purely AI-generated material, or material where there is insufficient human control over the expressive elements.
The Copyright Office's January 2025 report says prompts alone do not provide sufficient control. Human expression, creative selection and arrangement, or creative modifications can support protection.
In Thaler v. Perlmutter, decided on 18 March 2025, the D.C. Circuit upheld the human-authorship requirement for an autonomously generated image. The vendor's qualifying words deserve attention because there may be no copyright for it to assign.
For marketing copy or code you want to protect, preserve human drafts, substantive edits and version history. This is the US position; other jurisdictions differ, so for a particular asset, check with counsel.
Are we covered if AI output infringes someone's copyright?
Coverage depends on the product tier and exclusions, with several vendors excluding modified output. OpenAI's Service Terms name API customers and defined Enterprise customers; whether ChatGPT Business receives that output indemnity is unclear from the text.
| Vendor and tier | What is covered | What voids it |
|---|---|---|
| OpenAI API; ChatGPT Enterprise, Edu and Healthcare | Specified claims against use or distribution of output; Service-Specific Terms indemnity is uncapped | Known or foreseeable infringement; disabled or ignored safeguards; modification, transformation or combination; missing input rights; trademark use in commerce; Third Party Offering content |
| Anthropic paid commercial use | Specified third-party IP claims involving paid use | Customer modifications; outside technology combinations; inputs; known infringement; patented inventions in output; trademark use in commerce |
| Google listed paid indemnified services | Specified claims involving unmodified generated output | Likely infringement known to customer; ignored citations or filters; continued use after notice; trademark use; missing customization-data rights |
| Microsoft eligible products, including Azure OpenAI subject to conditions | Certain output IP claims under the Customer Copyright Commitment | Disabling, evading or interfering with content filters, metaprompt restrictions or other safety systems; use the customer knows or should know is likely to infringe; lacking sufficient rights to the input, including customization data; trademark claims from use in trade or commerce; for Azure OpenAI and configurable products, missing the Required Mitigations |
OpenAI's Service Terms exclude beta services and Prompt-to-Voice from indemnification. ChatGPT Business is separately named alongside the defined Enterprise products, so ask OpenAI to confirm your coverage.
Anthropic's commercial terms tie protection to paid use. Google's indemnified-services list includes Gemini in Workspace and the Gemini Enterprise Agent Platform API, but not the AI Studio Gemini API; free use does not qualify.
For Azure OpenAI, Microsoft requires specific mitigations, including a copyright metaprompt, evaluation with the report retained, and protected-material and jailbreak filters. Copilots with fixed safety systems do not require those customer mitigations.
Microsoft does not exclude modified output as such, and Copilot Studio and GitHub Copilot have their own mitigation sets.
The trap. Editing output is ordinary company practice, yet it can defeat protection under the OpenAI, Anthropic and Google terms. Paid-tier indemnity is conditional, trademark use is excluded, and for an actual claim or coverage decision, check with counsel.
What do we do when something goes wrong?
Our rule is to classify the incident, notify the assigned people within one hour and preserve evidence before cleanup. Every runbook entry needs a tested stop switch and a named notification decision-maker.
Use these five classes as our incident rules:
- Data exposure: tell the governance owner and privacy or security lead. Preserve the destination, account, content and time; revoke the connection or disable the affected route.
- Wrong output sent externally: tell the owner and responsible customer or publishing lead. Preserve the exact version and recipients; pause further publication or sending.
- Wrong automation action: tell the owner and affected process lead. Preserve action logs and identifiers; disable the trigger or relevant credential.
- Vendor incident or model change: tell the owner and technical maintainer. Preserve notices, model identifiers and failing examples; pause the affected workflow or invoke its approved fallback.
- Misuse or attack: tell the owner and security lead. Preserve prompts and access logs; isolate the integration or account.
For each class, our rule assigns external-notification decisions to the incident lead with privacy and legal advice. Record the prompt, output, account, time and tool tier with controlled access.
NIST GV-4.3-002 lists example incident-report fields using “such as”: system ID, title, reporter, system/source, data reported, incident date, description, impacts and affected stakeholders. These nine fields make a one-row incident log in the same spreadsheet as the inventory.
The hypothetical row records an employee pasting a customer complaint into a personal consumer chatbot account. Keep the customer's actual details in the access-controlled evidence record.
| System ID | Title | Reporter | System/Source | Data Reported | Date of Incident | Description | Impact(s) | Stakeholder(s) Impacted |
|---|---|---|---|---|---|---|---|---|
| AI-007 | Customer complaint exposure | Employee A | Consumer chatbot, personal account | Customer name and order history | DD Month YYYY | Employee pasted a complaint containing the customer's name and order history | Customer personal data disclosed to an unapproved tool; further exposure under assessment | Customer A; customer support team |
GDPR Article 33 generally requires authority notification within 72 hours where feasible, unless the breach is unlikely to create risk. Pasting customer personal data into a consumer tool may be reportable; assess it promptly.
For high-risk systems, Article 26(5) directs deployers to inform the provider first. Article 73's provider reporting clocks are generally 15 days, 10 days for death and two days for specified widespread or critical-infrastructure incidents. The clocks run from when the provider or, where applicable, the deployer becomes aware of the incident. Under Article 26(5), if the deployer cannot reach the provider, Article 73 applies to the deployer mutatis mutandis, so the same deadlines apply.
Use NIST SP 800-61 Rev. 3, published in April 2025, as the general incident-response reference. The human oversight controls address runtime failure modes, while automation maintenance procedures address model changes and silent quality drift; for notification obligations, check with counsel.
Does our insurance cover AI mistakes?
You cannot infer AI coverage from a policy's cyber or professional-liability label. Ask for the wording, because optional Verisk/ISO generative AI exclusions carry a January 2026 edition date.
The Independent Insurance Agents & Brokers of America description identifies CG 40 47 for Coverage A and B, CG 40 48 for Coverage B only, and CG 35 08 for products and completed operations. Their optional status does not tell you whether your insurer attached one.
Claims Journal reported on 20 July 2026 that Berkley introduced an absolute AI exclusion in D&O, E&O and fiduciary products. Fenwick describes cyber as the most stable source of AI-related coverage, while warning that output liability, IP and regulatory exposure may fall elsewhere.
Our rule is to send the broker these seven questions:
- Does any policy or renewal contain an AI exclusion, and how does it define AI?
- Which policy responds when our chatbot misinforms a customer?
- Is an employee's AI-related data leak covered, including through an unapproved tool?
- Are regulatory fines and defense costs covered where insurable?
- Does Tech E&O cover AI features we sell?
- Which AI application questions must we answer, and do our answers match the inventory?
- Will you provide the full endorsement text and identify the relevant insuring agreements?
Keep the response with the vendor and inventory records. A coverage summary is useful for finding the clause; the endorsement text determines what the clause says.
What is the order of work for the first month?
Our recommended sequence starts with the owner and discovery, then turns those findings into rules staff can apply. Finish with a runbook exercise and a broker review grounded in the actual inventory.
- →Name the owner
Give one person approval and suspension authority. Done means staff know the name and the person can stop an unsafe use.
- →Run the discovery
Export connected apps, inspect grants and reconcile spending with the amnesty survey. Done means each discovered use has an owner or an unresolved flag.
- →Write the policy
Answer our eight policy questions and attach the data table. Done means staff can identify the approved tier and reporting route.
- →Complete the inventory and vendor sheets
Record each tool and automation, including retention and DPA evidence. Done means unknown answers have a named person and deadline.
- →Brief staff and retain the record
Demonstrate prohibited inputs, human checks and hallucination risk. Keep attendance, materials and date as an internal literacy record.
- →Write and exercise the runbook
Assign notifications and test the stop switch on a safe example. Done means someone can suspend the workflow and preserve its evidence.
- →Call the broker
Send the inventory and our seven questions. Done means endorsement wording and unresolved coverage questions are stored with an owner.
Once the policy and inventory are usable, operations automation work can implement those decisions with scoped credentials and audit logging on every action. Make the permitted actions, stop switch and responsible reviewer explicit before connecting the workflow to a live company account.

Put your next steps in order
Build on what you have just read with a free ebook on semantic SEO and AI visibility. Get worked examples, decision rules, checklists and a do-this-week action in every chapter, plus a six-week plan for your site.