First-Party Data and Consent: A Reference

On this page
Analytics & Data
First-party data and consent are separate questions. Collecting data on your own site does not remove the need for a lawful basis to process personal data, and storing or reading information on a device generally needs consent unless an exception applies. GDPR Recital 30 names IP addresses and cookie identifiers as online identifiers, so an analytics setup can involve personal data without collecting a name.
Quick-reference table
| Term | What it means | Primary source | The trap |
|---|---|---|---|
| Personal data | Information relating to an identified or identifiable person | GDPR Art. 4(1), Recitals 26 and 30 | Cookie identifiers and pseudonymised data can qualify |
| Lawful basis | A permitted basis for processing personal data | GDPR Art. 6(1) | A basis for processing does not settle device storage |
| Consent | A freely given, specific, informed and unambiguous indication of wishes | GDPR Arts. 4(11) and 7(3) | A banner alone does not establish valid consent |
| Legitimate interest | A basis subject to a balancing test | GDPR Art. 6(1)(f), Recital 47 | Direct marketing is not automatically covered |
| Device storage consent rule | A rule governing storage of or access to information on a device | ePrivacy Art. 5(3); UK PECR regulation 6 and ICO exceptions guidance | A first-party analytics cookie is still device storage |
| CCPA sale and share | Transfers subject to California opt-out rights; sharing concerns cross-context behavioral advertising | California AG CCPA page; CCPA | Sale and share are separate concepts |
| Global Privacy Control | An opt-out preference signal a business that sells or shares must process | CCPA regulations, §7025(b) and (c)(1) | The opt-out extends to associated pseudonymous profiles |
| First-party data | Data a business collects on its own properties | GDPR Art. 4(1) for personal data | First party is an industry term, not a GDPR exemption |
| Third-party data | Data collected by another entity, including across sites | GDPR Art. 4(1) for personal data | The label does not determine controller or processor roles |
| Zero-party data | A marketing term for information a customer intentionally shares | GDPR Art. 4(1) for personal data | Voluntary sharing does not create a separate legal category |
| Consent mode | Google tag behavior based on consent choices; basic and advanced implementations differ | Google consent mode documentation | Consent mode does not collect the choice |
| Four consent parameters | Settings for advertising storage, user data, personalization and analytics storage | Google consent mode documentation | Granting one setting does not automatically grant the others |
| Behavioral modeling | Estimated behavior in GA4 when eligibility conditions are met | Google Analytics behavioral modeling page | Advanced mode alone does not guarantee modeled data |
| IP handling in GA4 | Google says GA4 does not log or store IP addresses | Google Analytics IP masking page | Other identifiers can still be personal data |
| Data retention | How long specified user and event data remains available under the GA4 setting | Google Analytics data retention page | The setting affects explorations and funnel reports |
| Data processing agreement | A contract or other legal act governing processing by a processor | GDPR Art. 28(3) | A vendor account does not make the agreement irrelevant |
| Data subject requests | Requests to exercise rights over personal data | GDPR Arts. 12 and 17 | Erasure applies where a listed ground exists |
| EU-US transfers | Transfers that may rely on an applicable adequacy decision | GDPR Art. 45; European Commission transfer page | The framework covers participating US companies |
| Hashed data and enhanced conversions | Hashed customer data used to match conversions with Google account data | GDPR Recital 26; Google Ads enhanced conversions page | A matchable email hash can remain personal data |
This is general information, not legal advice. Rules differ by jurisdiction; primary sources were read on 29 October 2026.
One analytics tag can raise three separate questions: whether information may be stored or read on a device, which lawful basis applies to personal data processing, and whether a California sale or share requires an opt-out. The applicable questions depend on the people, business and processing involved. The identity of the party that set a cookie answers none of them by itself.
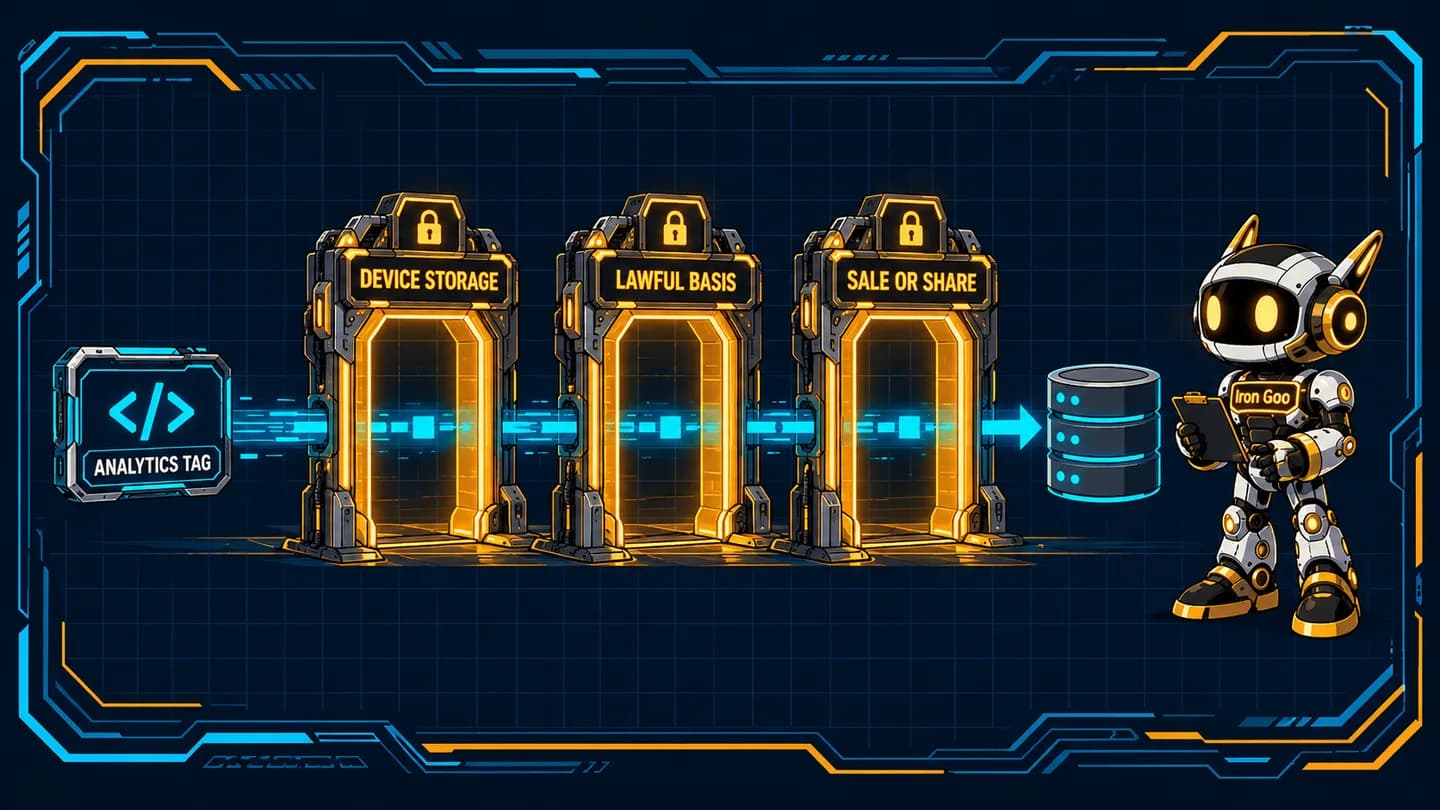
Each gate represents a separate rule. A choice at one gate does not automatically answer the questions at the others.
EU and UK legal terms
Personal data
GDPR Art. 4(1) defines personal data as “any information relating to an identified or identifiable natural person.” Recital 30 identifies online identifiers, including IP addresses and cookie identifiers. A name is therefore not a prerequisite for an analytics record to concern personal data.
Recital 26 says pseudonymised data that can be attributed to a person using additional information should be considered information about an identifiable person. Replacing an email address with a token can reduce exposure, but the ability to reconnect the token to a person remains part of the assessment.
Lawful basis
GDPR Art. 6(1) lists six lawful bases: consent, contract, legal obligation, vital interests, public task and legitimate interests. You need to identify the basis that fits the processing you actually perform. An analytics tag can involve more than one purpose, so write down the purpose and basis for each use of the data.
The lawful-basis question is separate from the device-storage question. Selecting legitimate interest for a processing purpose does not itself establish an exception to the rule on storing or accessing information on a device.
Consent
GDPR Art. 4(11) describes consent as “any freely given, specific, informed and unambiguous indication of the data subject's wishes.” A banner is a mechanism for presenting and recording a choice; its presence alone does not prove that the choice meets that standard or that tags respect it.
Article 7(3) says, “It shall be as easy to withdraw as to give consent.” Check the whole path: the initial choice, the saved preference and the later route back to change it. Withdrawal does not undo the lawfulness of processing carried out before withdrawal.
Legitimate interest
Article 6(1)(f) permits processing for legitimate interests subject to a balance against the person's interests and fundamental rights and freedoms. Recital 47 says direct marketing “may be regarded” as carried out for a legitimate interest. The word “may” leaves room for the assessment; it is not a blanket finding for every marketing use.
Record the interest you are pursuing and the balancing assessment for the actual processing. Then check device storage separately: a legitimate-interest assessment does not grant a cookie exception.
Device storage consent
The ePrivacy Directive, Art. 5(3), generally requires informed consent before storing information on, or accessing information already stored on, a user's device. It has two exceptions: carrying out a communication, and storage or access strictly necessary for a service the user explicitly requested. Analytics is not named among those exceptions; the directive is implemented in each EU member state's national law.
In the UK, PECR regulation 6 governs storage and access technologies. The ICO's exceptions guidance lists five exceptions: communication, strictly necessary use, statistical purposes, appearance and emergency assistance. The newer exceptions came with the Data (Use and Access) Act 2025, section 112, which added them to PECR as Schedule A1 and has been in force since 5 February 2026.
The statistical purposes exception has conditions. Collection must have the sole purpose of producing statistics about use of the service to improve it; the information must be aggregate, people must receive clear information and have a simple, free way to object, and a third-party provider must act as a processor without linking the data to other information it holds.
The ICO says advertising-related purposes, including ad measurement and performance, are not exempt from PECR's consent requirements and never have been. Our reading is that a setup linking analytics to advertising, or allowing a provider to use the data for its own purposes, would fail the processor condition. The ICO page does not name Google Analytics, so assess the actual settings and provider arrangements before relying on the exception.
California sale, sharing and opt-outs
CCPA sale and share
The California Attorney General's CCPA page explains that sharing refers specifically to sharing for cross-context behavioral advertising. Sale and sharing are separate concepts, so check both when mapping where personal information goes. For those activities, the CCPA uses an opt-out model; it does not generally require opt-in consent before collection, with separate rules for minors.
A business that sells or shares must provide the relevant “Do Not Sell or Share My Personal Information” link. A California visitor's opt-out is a request about sale or sharing, not a substitute for assessing the other purposes for which the business processes information.
Global Privacy Control
Global Privacy Control, or GPC, lets a browser or device send an opt-out preference signal. Under CCPA regulations §7025, a business that sells or shares personal information must process a qualifying signal as a valid opt-out for that browser or device and associated consumer profiles, including pseudonymous profiles.
The regulation says this processing is not required for a business that does not sell or share personal information. If you do sell or share, test the signal against your own tag and data flows: a visible link and a working browser signal are separate checks.
Applicability and California deadlines
For a for-profit business doing business in California, one applicable threshold is gross annual revenue over $26,625,000, the CPI-adjusted figure effective 1 January 2025. The AG page states the base $25 million figure; the California Privacy Protection Agency's adjustment supplies the higher amount.
Other thresholds include buying, selling or sharing personal information of 100,000 or more California residents or households, or deriving 50% or more of annual revenue from selling personal information. Meeting any one of the listed thresholds can bring a qualifying business within the CCPA's scope.
For requests to know or delete, respond within 45 calendar days. Another 45 days is available with notice. Honor an opt-out as soon as feasibly possible and no later than 15 business days.
Data collection vocabulary
First-party data
First-party data is an industry term for data a business collects on its own properties. An event recorded on your website or a preference submitted through your form may be described this way. The term says where the data came from; GDPR still asks whether it is personal data, who controls or processes it, and which lawful basis applies.
A first-party cookie set on your domain by a vendor's tag is still device storage. Before adding events, use a measurement plan to decide which questions require data at all. Collecting fewer unnecessary fields leaves fewer fields to protect and delete.
Third-party data
Third-party data is an industry description for data collected by another entity, including data gathered across sites. You may meet it when a vendor offers an audience segment or combines observations from multiple properties.
The label does not decide the legal roles. Examine what each organization does with the information and whether it acts as a controller or processor for the relevant purpose. Also check the device-storage rule where the collection relies on reading or writing information on a user's device.
Zero-party data
Zero-party data is a marketing term for information a customer intentionally and proactively shares with a brand, such as a preference submitted through a preference center. Salesforce's explanation credits Forrester Research with coining the term.
It is not a distinct GDPR category. Our reading of Art. 4(1) is that a preference relating to an identified or identifiable person is personal data, even when that person chose to provide it. Document the purpose for which you collected the preference and how the person can change it.
Hashed data and enhanced conversions
Google Ads enhanced conversions can use customer data such as email, name, home address and phone to supplement conversion tags. Google describes SHA256 as the one-way hashing algorithm used, and says it normalizes and matches the data with Google account data. The matching purpose is a reason to examine what the recipient can associate with the hash.
Our reading of GDPR Recital 26 is that a hashed email remains personal data where it can be attributed to a person using additional information. Hashing can reduce exposure; it does not automatically make a matchable value anonymous.
Do not treat an email hash as anonymous solely because the original address is not visible. Document the matching purpose, recipient and lawful basis for the data you send.
Google consent and analytics settings
Consent mode
Consent mode tells Google tags how to behave based on consent choices. It does not collect those choices. A banner or consent management platform must present the choice and pass the resulting state to the tags.
In Google's basic implementation, tags do not load until the user interacts with the banner. Without consent, no data reaches Google, including the consent status. In the advanced implementation, tags load with denied defaults and Google says, “While consent is denied, the Google tags send measurements without cookies.”
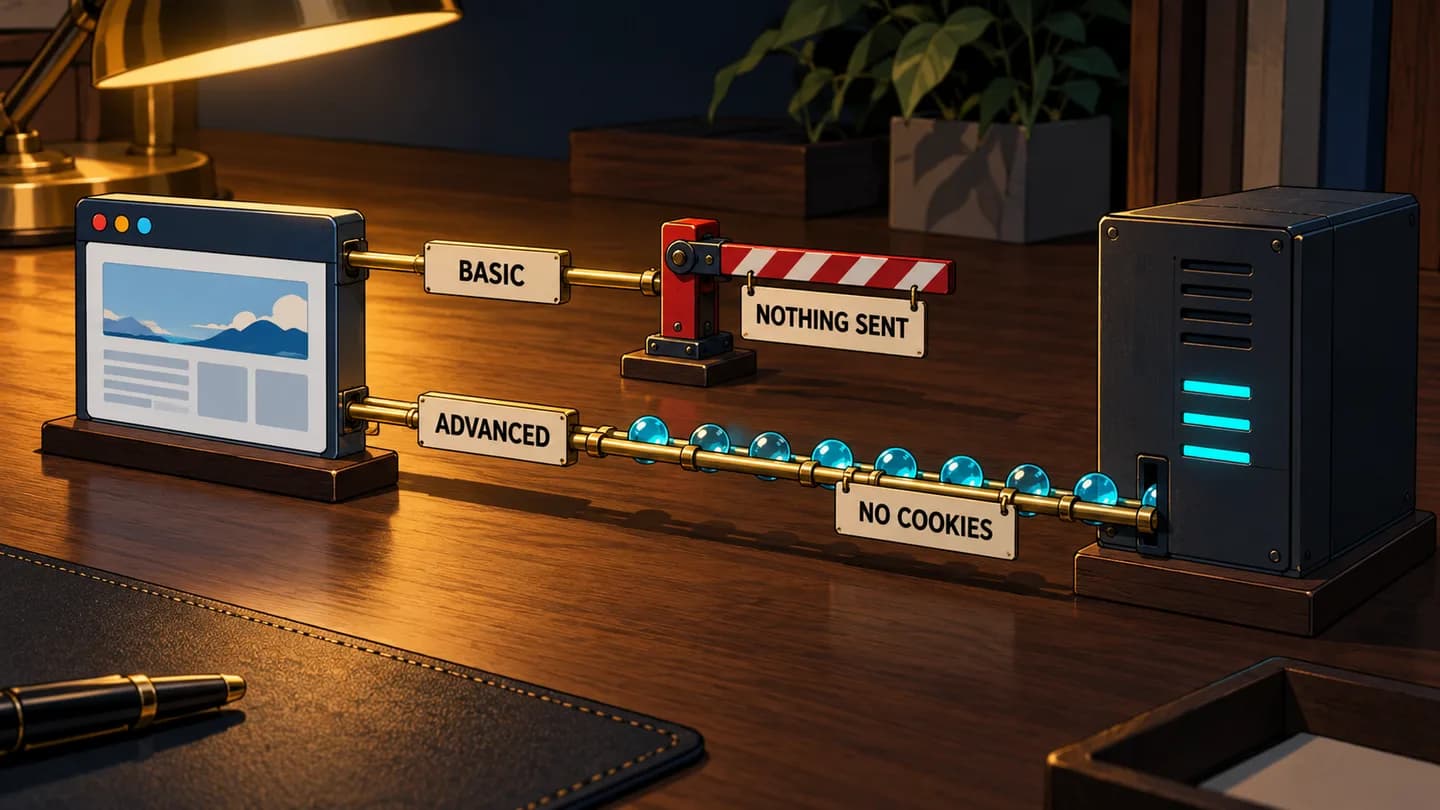
The two lanes show different behavior before consent. Basic mode blocks the tag; advanced mode sends cookieless measurements with denied defaults.
Advanced mode's cookieless measurements are still part of the processing you need to assess. Do not use the setting's name as a substitute for checking the applicable rules and your configuration.
The four consent parameters
Google describes the four parameters as follows:
| Parameter | Google's description |
|---|---|
ad_storage | “Enables storage, such as cookies (web) or device identifiers (apps), related to advertising.” |
ad_user_data | “Sets consent for sending user data to Google for online advertising purposes.” |
ad_personalization | “Sets consent for personalized advertising.” |
analytics_storage | “Enables storage, such as cookies (web) or device identifiers (apps), related to analytics, for example, visit duration.” |
The two advertising parameters concerning user data and personalization answer different questions. Keep them separate in your consent mapping, and update each state only when the corresponding choice supports it.
Set defaults before the Google tag configuration runs. This example starts all four parameters as denied:
gtag('consent', 'default', {
  'ad_storage': 'denied',
  'ad_user_data': 'denied',
  'ad_personalization': 'denied',
  'analytics_storage': 'denied'
});
The later consent update must reflect the person's actual selection. Iron Goo's website foundation build instruments analytics; the ordering of consent defaults and tags belongs in the implementation review.
Behavioral modeling
GA4 behavioral modeling has two traffic thresholds that must both be met. You need at least 1,000 events per day with analytics_storage denied for at least seven days, and at least 1,000 daily users sending events with analytics_storage granted for at least seven of the previous 28 days. Google also requires consent mode on all pages with the advanced implementation, and meeting the thresholds does not guarantee eligibility.
For a hypothetical site with 400 consented daily users, the second leg fails: 400 is less than 1,000. Without behavioral modeling, events from users who decline are not reported. Do not put an assumed recovery percentage into a forecast just because advanced mode is installed.
The small-business analytics reference explains the surrounding measurement vocabulary. Use the thresholds to decide whether modeled behavior is a realistic expectation for your property, then verify eligibility in the property itself.
GA4 IP handling
Google's IP masking documentation states: “In Google Analytics 4, IP masking is not necessary since IP addresses are not logged or stored.” The anonymize_ip setting belonged to Universal Analytics; it is not the GA4 setting to look for.
That statement does not make every GA4 record anonymous. Cookie identifiers can remain online identifiers under GDPR Recital 30, and the device-storage and lawful-basis questions still need answers.
Data retention
The GA4 retention setting offers two or 14 months for user-level data. Event data has two- or 14-month options on standard properties; Analytics 360 also offers 26, 38 or 50 months. Age, gender and interest data is retained for two months.
Google says, “The data retention setting only affects explorations and funnel reports.” The reset-on-new-activity option applies to user-level data, so inspect it along with the duration. Set the duration deliberately in Admin and include the decision in your data hygiene routine.
Google EU user consent policy
For end users in the EEA, UK and Switzerland, Google's policy requires consent for cookies or other local storage where legally required. It also requires consent for the collection, sharing and use of personal data for personalization of ads.
These are Google policy obligations alongside the legal rules applicable to your processing. Map each purpose to the choice presented to the user and to the tag setting that enforces that choice.
Obligations attached to the data
Data processing agreement
A data processing agreement sets out the terms under which a processor handles personal data for a controller. GDPR Art. 28(3) says, “Processing by a processor shall be governed by a contract or other legal act.” The article also requires the arrangement to specify matters such as the processing's subject, duration, nature and purpose.
For Google Analytics, an account-level Editor can review the terms at Admin > Account settings > Account details > Data Processing Amendment > Review Amendment. Google says new accounts accept the terms automatically, and its Google Ads Data Processing Terms replace the earlier Analytics amendment. Keep a record of the terms that apply to your account and the vendors that process data on your behalf.
Data subject requests
GDPR Art. 12(3) requires a response without undue delay and within one month of receiving a request. Where necessary, the period may be extended by two further months; tell the person about the extension within the first month.
For a hypothetical request received on 3 November, the ordinary response is due on 3 December. Log both dates when the request arrives, assign an owner and record where the relevant data must be searched.
Article 17 provides for erasure without undue delay where a listed ground applies. It is not an unconditional instruction to delete every record on request. Record the ground and the outcome of the assessment alongside the request.
EU-US transfers
GDPR Art. 45 permits a transfer where the European Commission has made an applicable adequacy decision. The Commission adopted the EU-US Data Privacy Framework adequacy decision on 10 July 2023; it covers US companies that participate in the framework. Check whether the particular recipient participates before treating the decision as applicable.
The General Court dismissed the Latombe challenge on 3 September 2025, and an appeal was lodged on 31 October 2025, as reported by WilmerHale. The Official Journal notice identifies the appeal as case C-703/25 P. As of 29 October 2026, the adequacy decision remains in force, the appeal is pending and no judgment was found; do not treat either the dismissal or the appeal as a prediction of the eventual result.
Checks to make in the implementation
Use these checks against the live site, the analytics account and the records your team maintains. Assign an owner to each failed check and record the date it was resolved.
- In Tag Assistant, confirm that consent defaults are denied before any Google tag fires.
- Open the banner and confirm that rejecting is as easy as accepting, as recommended in the ICO's consent guidance; return later and confirm that withdrawing is as easy as giving consent.
- In GA4 Admin, inspect the retention duration and reset-on-new-activity setting, and record the intended values.
- Inspect the account's data processing terms and record that the applicable agreement is accepted.
- Inspect URLs and event parameters for email addresses and phone numbers; use the tracking-plan guide to document permitted fields.
- If the business sells or shares personal information, send a GPC signal and verify that the opt-out is honored for the browser or device and its associated profile.
- Open the request log and confirm that each request has a received date, a due date and an assigned owner.
Start by opening Tag Assistant and checking the consent defaults before the first Google tag fires. Record what you observe before changing the configuration.

Put your next steps in order
Build on what you have just read with a free ebook on semantic SEO and AI visibility. Get worked examples, decision rules, checklists and a do-this-week action in every chapter, plus a six-week plan for your site.