Small Business Risk Management: 11 Failures and Fixes

On this page
- 1. One person holds a critical process
- 2. One customer supplies too much revenue
- 3. Cash runs short during a profitable period
- 4. A payment request impersonates a supplier or owner
- 5. A backup exists, but a restore fails
- 6. Employees put company data in personal AI tools
- 7. An AI answer makes a promise the company cannot keep
- 8. A vendor changes, retires or reprices a dependency
- 9. The insurance policy leaves a scenario unclear
- 10. One platform controls too many new leads
- 11. A customer-facing AI interaction lacks a disclosure
- Run a 60-minute risk review each quarter
Business
Small business risk management means finding the handful of ways a company of 10 to 200 people can get hurt, checking which exposures are present, and putting a specific control on each one. One useful starting point: the FBI IC3 2025 Internet Crime Report counted $3,046,598,558 in reported business email compromise losses from 24,768 complaints, second only to investment fraud by reported losses.
Many exposures are familiar: one person knows how to do the work, one customer supplies too much revenue, cash runs short, a payment request is faked, or a backup cannot be restored. AI adds company data in personal tools, incorrect chatbot promises, changing vendor services and disclosure obligations.
| Failure mode | One-line confirm check | Trigger to act |
|---|---|---|
| Key-person dependency | Count who can complete each of ten revenue or payroll processes without the usual operator. | Any process has only one capable person. |
| One big customer | Divide the largest customer's trailing 12-month revenue by total revenue. | Above about 25%, our rule of thumb. |
| Cash shortfall | Calculate days cash on hand and the low point in a 13-week forecast. | For a seasonal firm, less than 30 days or a forecast below zero without a credit line, our rule of thumb. |
| Payment fraud | Check the last 12 months of payee bank-detail changes for documented callbacks. | Any change lacks verification using a number already on file. |
| Ransomware and untested backup | Restore one important file and one whole system to a separate machine. | Either restore fails or its retrieval and restore times are unknown. |
| Company data in AI tools | Ask teams about tools and account types; inspect expenses for subscriptions. | Company data enters a personal account or unapproved tool. |
| AI output errors | Compare answers to 20 common policy questions with written policy. | An answer conflicts with policy or makes an unsupported promise. |
| Vendor lock-in or shutdown | List each automation's model or API, vendor, renewal date and export option. | A dependency has no usable export, replacement plan or known review date. |
| Insurance gaps | Ask the broker for written coverage and sublimits for the scenarios you face. | A needed answer, coverage term or sublimit is unclear. |
| Platform dependency | Calculate each source's share of new leads or revenue over 12 months. | One channel supplies more than half of new leads, our rule of thumb. |
| Regulatory change | List customer-facing AI touchpoints and inspect the first interaction. | An applicable touchpoint lacks a clear AI disclosure. |
The order is Iron Goo's judgement of how often owners meet these exposures, not a measured frequency ranking.
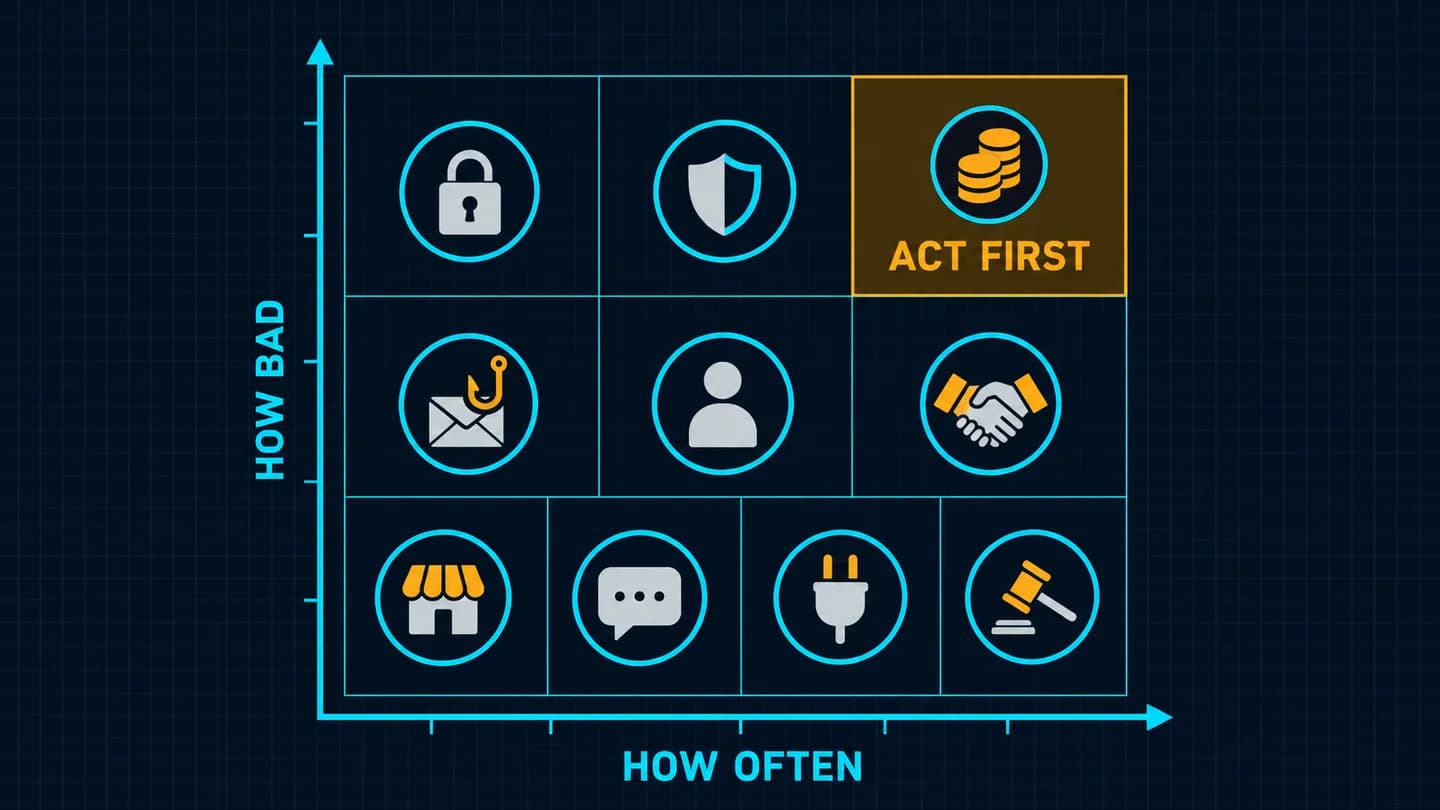
This illustrative grid is not a measured ranking and does not show every failure mode. Start with risks in the upper right, where frequent and severe meet.
1. One person holds a critical process
Symptom: Work stops or waits when one person is off. That person may be the only one who knows the supplier logins, can approve pricing exceptions or can close out a job.
Cause: A process can grow around the person who built it. The steps may be partly documented while the decisions, permissions and credentials remain in that person's head or personal accounts.
How to confirm: List the ten processes that produce revenue or pay people. For each, count the people who can complete it end to end without the usual operator. Someone who can find the spreadsheet but cannot make the decision does not count. Any process with a count of one is an exposure; the output is a ten-row list with a count beside each process.
Fix: Assign one Accountable owner and a trained backup to each exposed process. Put shared credentials in a company password manager and have the backup perform the work using the written procedure. An SOP passes when another person produces the right result without the author filling gaps aloud.
The process and SOP guide explains how to write and test that procedure. If the internal work needs an operations layer, Iron Goo's operations service follows an audit, build, operate model for agentic internal operations, with monthly reports on what changed.
2. One customer supplies too much revenue
Symptom: One customer accounts for a large share of sales, and its renewal date receives more attention than the rest of the pipeline. A late payment or a change in that customer's purchasing plans can alter the company's cash position.
Cause: Winning a large account can be a strength. The exposure is having no plan for losing it: fixed costs and staffing may have grown around revenue that depends on one contract.
How to confirm: Pull trailing 12-month revenue from accounting. Divide revenue from the largest customer by total revenue for the same period. In a hypothetical company, $540,000 divided by $1,800,000 equals 30%.
Our rule of thumb is to put new-business pipeline on the weekly list when that share rises above about 25%. For context, FASB ASC 280 requires US public entities to disclose the total revenue from any single external customer that accounts for 10% or more of revenue, without naming that customer. That disclosure threshold shows what investors are told; it is not a universal limit for a private company.
Fix: Review the pipeline every week and assign responsibility for developing other customer relationships. Put the large customer's renewal date and notice period on the calendar, and read the contract terms before planning around renewal. Keep serving the account well while building a practical response to losing it.
3. Cash runs short during a profitable period
Symptom: The income statement shows a profit, yet payroll week is tight. Cash can arrive after the bills it needs to pay, and an annual profit figure does not identify the week when the bank balance is lowest.
Cause: Revenue, expenses and cash movements do not always land in the same period. A company with seasonal demand or uneven customer payments can have a cash problem before its annual results show one.
How to confirm: Calculate days cash on hand as cash divided by annual cash operating expenses divided by 365. In a hypothetical example, $60,000 divided by ($1,460,000 divided by 365, or $4,000 a day) equals 15 days. Record both the cash balance and the expense period used so the next calculation is comparable.
The JPMorgan Chase Institute study, published in September 2016, examined 597,000 small businesses using transaction data from February through October 2015. The median cash buffer was 27 days, and one quarter held fewer than 13 days. Those are observations from one bank's customers in 2015, not a target.
Fix: Maintain a rolling 13-week cash forecast with expected receipts, payments and a closing balance for each week. Iron Goo's opinion, offered as a rule of thumb for a seasonal firm, is to hold 30 days of cash operating expenses and keep the forecast's lowest closing balance above zero without drawing a credit line. The cash and financial resilience guide works through the 13-week forecast.
4. A payment request impersonates a supplier or owner
Symptom: A supplier emails new bank details, or someone appearing to be the owner asks for a wire to be sent urgently. The request may arrive in an existing conversation and look routine to the person processing it.
Cause: IC3 describes business email compromise as a scheme targeting businesses or individuals working with suppliers or regularly making wire payments. It can involve compromised email accounts and other communications, including phone numbers and virtual meeting applications. IC3 reported more than $30 million in AI-involved BEC losses in 2025 and says not all BEC tactics use AI; most of the reported BEC losses were outside that AI-involved figure.
How to confirm: Pull every change of payee bank details from the accounting system for the last 12 months. For each change, check whether the record shows a verification call to a number already on file. The resulting list should identify every change with missing verification.
Before paying changed bank details received by email, call a number already on file. Do not use a phone number supplied in the email.
Fix: Require that callback for new or changed bank details and require a second person to approve them. Enable multifactor authentication on email, as IC3 recommends. Record who called, the number used and who approved the change.
The callback uses the supplier number already on file, and a second person approves the new details before payment.
If money has gone, IC3 says to contact your bank immediately and request a recall, then file a complaint at ic3.gov regardless of the amount. In 2025, IC3's Recovery Asset Team Financial Fraud Kill Chain handled 3,900 incidents, froze $679,013,183 and reported a 58% success rate. In April 2025, an Oregon city government office had a $6 million wire recalled: the recipient account had been flagged in an earlier Financial Fraud Kill Chain, so the recipient bank asked the originating bank to confirm the wire instructions, which were found to be fraudulent.
5. A backup exists, but a restore fails
Symptom: The company has a backup subscription or a drive in an office, but nobody can say when an important file or a whole system was last restored. A backup status indicator alone does not tell you how long recovery takes or whether the restored system works.
Cause: Backups can be incomplete, inaccessible or affected by the same network incident as the original. Recovery also depends on access to the backup service and the credentials needed to use it.
How to confirm: Restore one important file and one whole system to a separate machine. Record the time to retrieve each backup and the time to restore it, then check that the file opens and the system works. The NIST NCCoE ransomware recovery guide calls for testing backup integrity and recording retrieval and recovery times.
IC3 counted more than 3,600 ransomware complaints in 2025 and over $32 million in reported losses. IC3 says that figure normally excludes items such as lost business, time, wages, files, equipment and third-party remediation, and that some victims report no loss amount at all, which makes the overall ransomware loss rate artificially low.
Fix: Apply the 3-2-1 rule, which the NIST NCCoE guide cites from US-CERT's backup recommendations: keep three copies of any important file, one primary and two backups, on two different media types, with one copy stored off-site. CISA's data backup guidance presents the same rule. Keep one copy disconnected from the business network and cloud provider admin credentials offline. Enable multifactor authentication on webmail, VPN and critical accounts, and repeat the restore test on a schedule.
6. Employees put company data in personal AI tools
Symptom: Staff paste customer emails, contracts or spreadsheet contents into personal ChatGPT or Claude accounts to complete work. A company may discover the tools only after noticing a subscription on an expense report.
Cause: People can adopt useful tools before the company has chosen an account, agreed on data handling or written a policy. Microsoft and LinkedIn's 2024 survey found that 78% of AI users brought their own AI tools to work; the figure was 80% at small and medium-sized companies. Press reports said Samsung banned generative AI on company devices and networks in 2023 after staff uploaded source code. That was a reaction to an incident, not evidence that bans eliminate use.
How to confirm: Ask each team which AI tools it uses and whether the accounts are personal or company-managed. Check expense reports and card statements for AI subscriptions. Produce a list of tools, account types and the categories of company information entered into each.
Fix: Approve company-account business tiers or an API with terms that prohibit training on company data. The OpenAI API data controls page says API data is not used for training by default unless the customer opts in, and abuse monitoring logs are retained for up to 30 days.
Set a rule that personal accounts and personal API keys are never used for company data. A paid consumer subscription is still a consumer subscription. The AI governance guide sets out a written policy and data classes you can adapt.
7. An AI answer makes a promise the company cannot keep
Symptom: A chatbot or AI-drafted email gives a customer a refund, price, delivery or warranty answer that conflicts with the written policy. The answer may sound confident and include details that nobody authorized.
Cause: A system can produce an answer that does not match the source policy, or it can draw on an outdated version. Publishing the answer through a chatbot does not remove the company's responsibility for the information it provides.
In Moffatt v. Air Canada, 2024 BCCRT 149, decided 14 February 2024, the chatbot described a 90-day retroactive bereavement claim that contradicted the linked Bereavement travel page. The tribunal found negligent misrepresentation and ordered C$812.02 in total: C$650.88 in damages, C$36.14 in interest and C$125 in tribunal fees.
It should be obvious to Air Canada that it is responsible for all the information on its website. It makes no difference whether the information comes from a static page or a chatbot.
The amount was small. The decision illustrates the responsibility a company can bear for what its chatbot says.
How to confirm: Run the chatbot or AI email drafts against the 20 most-asked policy questions, including refunds, prices, delivery and warranty. Compare every answer with the current written policy and record each conflict or unsupported promise. The output is a 20-row test with the answer, policy reference and result.
Fix: Ground answers on current policy pages and route anything promising money or contractual terms through a human review gate. Give customers a visible path to a person. Retest the affected questions whenever the underlying policy changes.
8. A vendor changes, retires or reprices a dependency
Symptom: An automation depends on a particular model, API or software plan, but nobody knows its renewal date or what would happen if the service changed. A vendor notice may reach an inbox without reaching the person responsible for the workflow.
Cause: Tools and model versions have their own release and retirement schedules. Data can also become difficult to move if the company has not checked what its vendor will export or whether another system can use the result.
How to confirm: Inventory every automation with the model ID or API it calls, the vendor, the renewal date and whether data can be exported in a usable format. Add any announced retirement date and the person responsible for checking it. The deliverable is a dependency list with missing exports or replacement plans visible.
OpenAI's deprecations page says it gives at least six months' notice for generally available models and at least three months for specialized variants. Preview models may be retired with notice as short as two weeks. The page lists gpt-4.5-preview with its deprecation announced on 14 April 2025 and shutdown on 14 July 2025. It also lists the Assistants API notice on 26 August 2025 and shutdown on 26 August 2026.
Fix: Put a calendar reminder in place to read each vendor's deprecation page. Keep prompts and data in your own systems, verify the export can be used, and test one alternative before you need it. Include pricing and renewal terms in the review so a repricing notice has an owner.
9. The insurance policy leaves a scenario unclear
Symptom: The company has cyber insurance, but nobody can identify the coverage or sublimit for a fraudulent wire, a vendor-held data breach or a business interruption. A policy name does not answer those questions.
Cause: Coverage depends on the policy wording. The FTC's small-business guidance on cyber insurance describes first-party coverage as protecting your data and typically covering items such as forensics, data recovery, customer notification, lost income from business interruption, and cyber extortion and fraud. Third-party coverage generally protects against liability when a third party brings claims against you.
The FTC checklist includes attacks on your data held by vendors, attacks anywhere in the world and duty to defend wording. It does not name social engineering or funds-transfer fraud. Our reading is that whether a tricked wire is covered depends on the policy's wording.
How to confirm: Ask your broker in writing which first-party and third-party items are covered, which sublimits apply, whether vendor-held data and attacks worldwide are included, and what duty to defend wording applies. Ask specifically about a fraudulent transfer caused by an impersonated payment request. Compare the answers with your payment-fraud and ransomware exposures, and keep the written response with the policy.
Fix: Adjust or buy coverage after putting the payment and backup controls in place. Our reading is that you should be ready to describe controls such as multifactor authentication and backups when discussing coverage. Ask the broker to explain the actual policy and its exclusions; do not assume any particular insurer or policy treats the scenario the same way.
10. One platform controls too many new leads
Symptom: Most new inquiries arrive from one marketplace, ad channel or search engine. A change in that source can reduce inquiries before the company has another dependable way to reach prospective customers.
Cause: A platform controls parts of the system that sends traffic or leads. Google says it makes significant, broad changes to its search algorithms and systems several times a year. Its core update guidance, last updated 10 December 2025, explains how to assess a change.
How to confirm: Calculate the share of new leads or revenue from each source over the last 12 months. Use consistent source labels and record unknown sources separately so the calculation does not hide gaps. Our rule of thumb is that a channel supplying more than half of new leads gets a second channel on the plan.
For a suspected Google core update effect, check the start and end dates on the Google Search Status Dashboard. Google advises waiting at least a full week after the update completes before analyzing performance in Search Console, then comparing with a week before the update started. Avoid quick-fix changes during that assessment.
Fix: Maintain an email list the company controls and develop a second acquisition channel. Assign an owner and a review date to that channel, then track its leads separately. When search traffic falls during a core update, wait for the update to finish and use the comparison period before changing pages in response.
11. A customer-facing AI interaction lacks a disclosure
Symptom: A customer starts a conversation with an AI chatbot and receives no clear indication that the interaction is with AI. The company may have added the tool to several pages without an inventory of where customers meet it.
Cause: A product can be deployed before someone checks which disclosure rules apply to the people it serves. For companies whose chatbot serves people in the EU, EU AI Act Article 50 requires providers to ensure that people interacting directly with an AI system are informed, unless that is obvious.
Article 50(5) calls for the information to be clear and distinguishable at the first interaction or exposure. Article 50 applies from 2 August 2026 under Article 113, as amended by Regulation (EU) 2026/1744.
How to confirm: List every customer-facing AI touchpoint and open each one as a customer would. Record whether the first interaction clearly tells the person they are talking to AI. The result is a list of touchpoints with the disclosure text or a recorded gap.
Fix: Add a clear disclosure line at the first message and name a person to read regulator updates once a quarter. Ask counsel how the requirements apply to your systems and customers.
Run a 60-minute risk review each quarter
The owner can rerun the eleven checks in a 60-minute quarterly review by collecting the current figures and test results in advance. Write each result in one table with the exposure, evidence, owner, control and next review date. The guide to building a business worth selling explains why buyers examine the same concentration, key-person and documentation exposures.
- Check the ten-process list for any process with one capable person, then record the backup and the date of its last successful SOP test.
- Recalculate the largest customer's revenue share, days cash on hand and the lowest closing balance in the 13-week forecast. Record the figures and the dates used.
- Inspect payee bank-detail changes for callback evidence and second-person approval. Record the latest file and system restore results, including retrieval and restore times.
- Update the AI tool and account inventory, then record the results of the 20-question customer-policy test.
- Check the automation inventory for vendor notices, renewal dates, usable exports and an alternative test. Request written broker answers for any unresolved coverage or sublimit.
- Recalculate lead sources, inspect first-contact AI disclosures and record who will review regulator updates before the next quarter.

Put your next steps in order
Build on what you have just read with a free ebook on semantic SEO and AI visibility. Get worked examples, decision rules, checklists and a do-this-week action in every chapter, plus a six-week plan for your site.