How to Build an Email List for a Small Business

On this page
- 1. Authenticate the sending domain: SPF, DKIM and DMARC records
- 2. Meet Gmail and Yahoo sender rules
- 3. Build a double opt-in signup path and keep consent records
- 4. Write a welcome sequence a small team can run
- 5. Clean the list: bounces, suppression and a sunset policy
- 6. Measure clicks, replies and conversions without trusting opens
Marketing
Litmus counted Apple as 76.56% of the more than 1.5 billion email opens measured in September 2026. To build an email list for a small business, authenticate your sending domain, collect consented signups through double opt-in, send a short welcome sequence, remove bounces and inactive addresses, and measure clicks and replies. The plumbing matters because an open is a shaky measure of whether anyone read your message.
Litmus says that when Mail Privacy Protection is on, you cannot know whether that user opened your email. It includes privacy-impacted opens in its Apple Mail figure. Our reading is that this inflates the 76.56% figure: Apple says Mail Privacy Protection downloads remote content privately in the background, which can register an open without a person reading the message. Its protection does not extend to links or attachments. The Litmus report cites studies showing that Mail Privacy Protection affects roughly 55% to 60% of all email opens.
An email list gives you a direct route to subscribers without asking a social platform for permission to show each message. It is one of several marketing channels a small team can run, provided someone owns the signup path and the routine checks.
1. Authenticate the sending domain: SPF, DKIM and DMARC records
Do this: Publish the records supplied by your email service provider, or ESP, in your domain's DNS. SPF identifies authorized sending infrastructure, DKIM lets the receiver verify a signature on the message, and DMARC tells the receiver what policy applies when authentication does not align with the visible From domain.
The following records are examples. Replace them with the values your ESP gives you, including its DKIM selector and CNAME target. The example IP address is reserved for documentation and is not a working mail server.
example.com.                TXT   "v=spf1 ip4:192.0.2.25 include:_spf.esp.example -all"
s1._domainkey.example.com.  CNAME s1.dkim.esp.example.
_dmarc.example.com.         TXT   "v=DMARC1; p=none; rua=mailto:[email protected]"
Start DMARC at p=none and inspect aggregate reports for legitimate senders that fail alignment. Once you have corrected them, move to p=quarantine, monitor again, and then move to p=reject. Gmail accepts p=none for its bulk-sender requirement, but that policy does not ask receivers to quarantine or reject failing messages.
RFC 9989, published in May 2026, obsoleted RFC 7489 and removed the pct tag. It adds t=y test mode, which replaces the pct=0 use: receivers apply one level below the published policy, treating p=quarantine; t=y as none and p=reject; t=y as quarantine. It is not a percentage ramp; use it where supported if you need to test a policy, while recognizing that receiver support may vary.
Check: Query the public records, then send a test message through your actual ESP to a mailbox you control. In Gmail, open the message and choose Show original to inspect its authentication results.
dig +short TXT example.com
dig +short CNAME s1._domainkey.example.com
dig +short TXT _dmarc.example.com
Expected: Your real domain's output should contain one SPF policy, the ESP's DKIM target, and a DMARC policy. The output for the example records would look like this:
"v=spf1 ip4:192.0.2.25 include:_spf.esp.example -all"
s1.dkim.esp.example.
"v=DMARC1; p=none; rua=mailto:[email protected]"
A receiving server can add an Authentication-Results header like this:
From: Example <[email protected]>
Authentication-Results: mx.example.com;
  dkim=pass header.d=example.com header.s=s1;
  spf=pass [email protected];
  dmarc=pass header.from=example.com
Read each result against the visible From domain. dkim=pass means the signature verified, and header.d=example.com identifies the DKIM signing domain, which is what DMARC alignment checks. spf=pass means the sending IP was authorized for smtp.mailfrom; here its organizational domain matches example.com. DMARC passes when at least one passing method also aligns with the From domain: under relaxed alignment, the organizational domains must match.
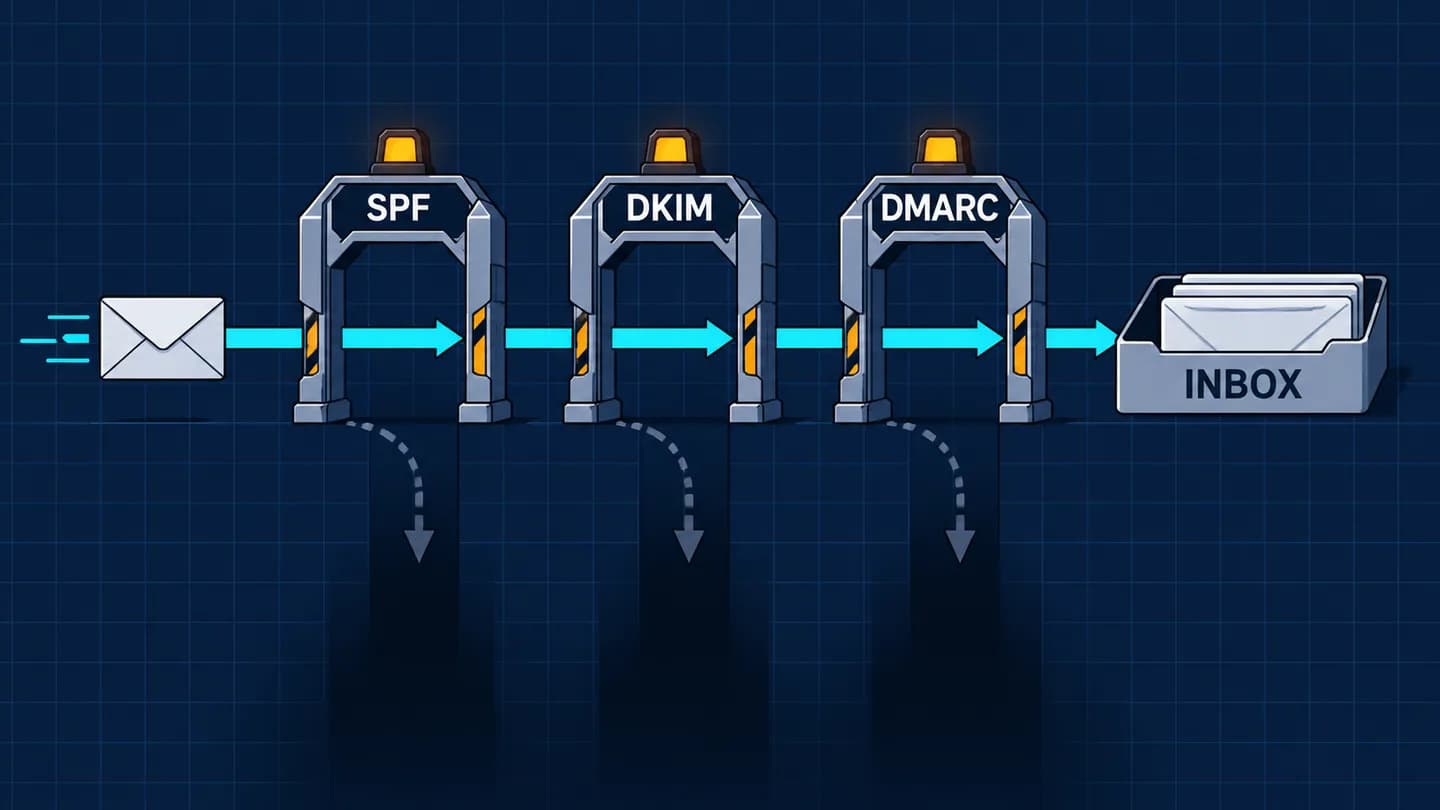
Notice the separate authentication checks before delivery. A passing signature or SPF check also needs the right domain alignment for DMARC.
Bad result: Two separate TXT records beginning v=spf1 can cause SPF to fail. Combine authorized senders into one policy, and check its expanded evaluation: RFC 7208 section 4.6.4 limits SPF to 10 DNS-querying terms, including include, a, mx, ptr, exists and redirect; exceeding that limit produces permerror. An empty _dmarc answer means no DMARC record was found at that name.
Individual passes do not guarantee DMARC alignment. In this example, both methods pass for the ESP's domain, while the visible From domain is example.com:
From: Example <[email protected]>
Authentication-Results: mx.example.com;
  dkim=pass header.d=esp.example;
  spf=pass [email protected];
  dmarc=fail header.from=example.com
Ask the ESP to configure an aligned DKIM signing domain or an aligned envelope sender, then repeat the test. For Gmail, DKIM keys must be at least 1,024 bits; Google recommends 2,048 bits.
2. Meet Gmail and Yahoo sender rules
Do this: Apply the all-sender requirements even if your list is small. Since February 1, 2024, Gmail has required all senders to use SPF or DKIM, valid forward and reverse DNS, TLS, correctly formatted messages and a Postmaster Tools spam rate below 0.30%.
If you send more than 5,000 messages a day to Gmail, the Gmail sender guidelines also require SPF, DKIM and DMARC, with the From domain aligned to SPF or DKIM. Messages from the same primary domain count together, and crossing the threshold once makes you a bulk sender permanently. Google began ramping up enforcement in November 2025, including temporary and permanent rejections.
For marketing and subscribed messages, configure one-click unsubscribe and keep a visible unsubscribe link in the body. Transactional messages such as password resets and reservation confirmations are excluded from Gmail's one-click requirement. Yahoo's bulk-sender guidance also calls for authentication, alignment, a visible link and one-click unsubscribe; Yahoo highly recommends the RFC 8058 POST method and accepts mailto.
Check: Inspect the raw headers of a marketing message and confirm that a valid DKIM signature covers both unsubscribe headers. Then send a bare POST to the HTTPS endpoint for a test subscriber. The example address and token are placeholders; use your own test endpoint.
List-Unsubscribe: <https://example.com/u/7f3c9a2e>, <mailto:[email protected]?subject=7f3c9a2e>
List-Unsubscribe-Post: List-Unsubscribe=One-Click
curl -i -X POST -d 'List-Unsubscribe=One-Click' https://example.com/u/7f3c9a2e
Expected: The endpoint returns a successful response, and your subscriber record changes to unsubscribed without a login or confirmation page.
HTTP/2 204
Subscriber status: unsubscribed
The status line is an example HTTP response; verify the subscriber status separately in your ESP. RFC 8058 requires an HTTPS URI, the POST body shown above, and a valid DKIM signature covering both headers. The POST must work without cookies, HTTP authorization or other context, and the sender must not return an HTTPS redirect. A GET should not unsubscribe by itself, because link scanners can fetch links.
Bad result: A 302 to a login page or a 405 response means the one-click POST did not complete the job. A successful response with the subscriber still active is also a failure. Check the ESP's suppression record as well as the HTTP response.
Google recommends honoring requests within 48 hours, Yahoo says within two days, and CAN-SPAM allows 10 business days. Iron Goo's opinion is to meet the shortest deadline for every recipient. CAN-SPAM also requires a valid physical postal address, an opt-out mechanism that works for at least 30 days after sending, and an opt-out without a fee or a requirement for more than an email address.
In Google Postmaster Tools, check Compliance status and Spam rate. Compliance status can show Compliant, Needs work or No data found; a fix can take up to seven days to appear. Google recommends a spam rate below 0.10%, which works out to one complaint per 1,000 qualifying inbox deliveries. At 0.30%, three complaints per 1,000 reach the ceiling; above 0.30%, a bulk sender is ineligible for mitigation until the rate stays below 0.30% for seven consecutive days.
3. Build a double opt-in signup path and keep consent records
Do this: Put a signup form where the offer is relevant. State what subscribers will receive and how often, then send a confirmation email immediately. Its one job is to explain what the person requested and provide a confirm button; leave marketing content out.
Add the address to the active mailing audience only after confirmation. Double opt-in is not generally required by GDPR or CAN-SPAM, but it provides evidence that the person controlling the address requested the subscription and that the address works. Where processing relies on consent, GDPR Article 7(1) requires the controller to be able to demonstrate that consent.
Check: Submit a test address through the public form. Check the message's arrival time and spam folder, follow the confirm button, and inspect the resulting subscriber and consent records.
Expected: Before the click, the address is pending and receives no campaign. After the click, it is active with a record comparable to this hypothetical example:
{
  "email": "[email protected]",
  "consent_text_version": "newsletter-v1",
  "form_url": "https://example.com/newsletter",
  "signed_up_at": "2026-10-29T12:00:00Z",
  "confirmed_at": "2026-10-29T12:01:00Z",
  "confirm_ip": "192.0.2.42",
  "source": "website signup form"
}
Keep the actual wording associated with consent_text_version, along with the form URL and timestamps. The confirmation IP is optional; the record should let you connect a subscriber to the offer and wording they accepted.
Bad result: A confirmation that arrives minutes late or lands in spam can leave a willing subscriber stuck before activation. Check delivery and authentication, then repeat the test. An address appearing in the active campaign audience before confirmation means the flow is bypassing the consent check; keep it pending until the confirmation event is recorded.
4. Write a welcome sequence a small team can run
Do this: Write the sequence once, assign an owner, and review its links and promises quarterly. Iron Goo's opinion is to use the confirmation plus three short emails on this schedule:
| When | One job | Check | |
|---|---|---|---|
| Confirmation | Immediately after signup | Get the subscriber to confirm | Button records confirmation |
| Welcome | Immediately after confirmation | Deliver the promised item and invite one reply | Promise link works; reply goes to a monitored inbox |
| Useful resource | Day 3 | Send one strong existing resource | Link opens the intended page |
| How you work | Day 7 | Explain your approach with a verifiable example or proof | Every claim can be checked |
The welcome email can ask a simple question related to the signup promise, such as what the subscriber is trying to solve. Replies give you a direct signal of engagement and a subject for follow-up. Use a real, supportable example in the day-seven email; if you have no proof you can publish, explain the process plainly.
Check: Run a test subscriber through the entire automation with a controlled clock or the ESP's test function. Confirm that the welcome email cannot fire before confirmation and that replies reach an inbox someone reads.
Expected: The automation log shows one event for each step, with the promised delays and no duplicate sends.
signup: pending
confirmation: sent
confirmation: completed
welcome: sent
resource: scheduled for day 3
how you work: scheduled for day 7
Bad result: A welcome message sent while the address is pending indicates the trigger is wrong. A broken promise link or an unmonitored reply address makes the first message less useful, even if delivery succeeds. After the sequence, use your content marketing demand engine to choose material for the regular cadence subscribers were promised.
5. Clean the list: bounces, suppression and a sunset policy
Do this: Suppress hard bounces immediately and keep a suppression list across imports and sending tools. A hard bounce indicates a permanent delivery problem; repeatedly mailing that address will not repair it. Soft bounces can be temporary, so check your ESP's documented handling before setting a rule.
For example, Mailchimp documents immediate removal of hard bounces in most cases. It marks an address cleaned after seven soft bounces when there is no subscriber activity, or up to 15 when there has been prior activity. Those are Mailchimp's rules, not a universal threshold for every provider.
Iron Goo's opinion for a sunset policy is to send one re-engagement email after 90 days without a click, then suppress the address at day 120 if there is still no click. The re-engagement email should have one clear click to stay subscribed. Use clicks for this rule because privacy-affected opens cannot reliably show that someone read a message.
Check: Inspect the bounce and suppression reports after each send. Test an import containing an address already on the suppression list, and check the automation's selection criteria for the 90-day and 120-day jobs.
Expected: A hard-bounced or unsubscribed address stays suppressed after import. A subscriber who clicks the re-engagement link remains eligible; one with no qualifying click by day 120 is suppressed.
hard bounce: suppressed
unsubscribed: suppressed
no click for 90 days: re-engagement sent
no click by day 120: suppressed
suppressed address imported again: remains suppressed
Bad result: A suppressed address becoming active after an import exposes a gap between systems. Deleting the suppression record creates the same risk on a later import. Bounce and suppression sync, sunset re-engagement and consent logging are recurring jobs an operations layer can run.
6. Measure clicks, replies and conversions without trusting opens
Do this: Record clicks per delivered message, reply count, unsubscribes and complaints for each send. Tag links with UTM parameters so you can connect a campaign visit to a lead or conversion in your analytics and customer records. Keep the definition of each metric beside the report, especially its denominator.
click_rate = unique_recipients_who_clicked / delivered_messages * 100
For a hypothetical send, 2,000 messages delivered and 50 recipients clicking gives 50 / 2,000 * 100 = 2.5%. Count a recipient once for this calculation even if they click several links. Track replies separately, and use marketing measurement without a data team to connect tagged visits to leads and revenue.
Check: Compare the ESP's send report with the Spam rate and Compliance status dashboards in Google Postmaster Tools. Check that a tagged link reaches the intended landing page and that the campaign identifier is retained when a visitor becomes a lead.
Expected: Your report identifies the send, delivered count, unique clickers, replies, unsubscribes, complaints and attributed conversions.
send: welcome-resource
delivered: 2000
unique recipients who clicked: 50
click rate per delivered: 2.5%
replies: 8
unsubscribes: 4
complaints: 1
UTM-attributed leads: 3
These figures are a hypothetical example, not a benchmark. Google Postmaster Tools calculates its spam rate from messages delivered to an engaged recipient's inbox and then marked as spam. An ESP rate using all sent messages as its denominator can therefore read lower; compare the definitions before treating the figures as equivalent.
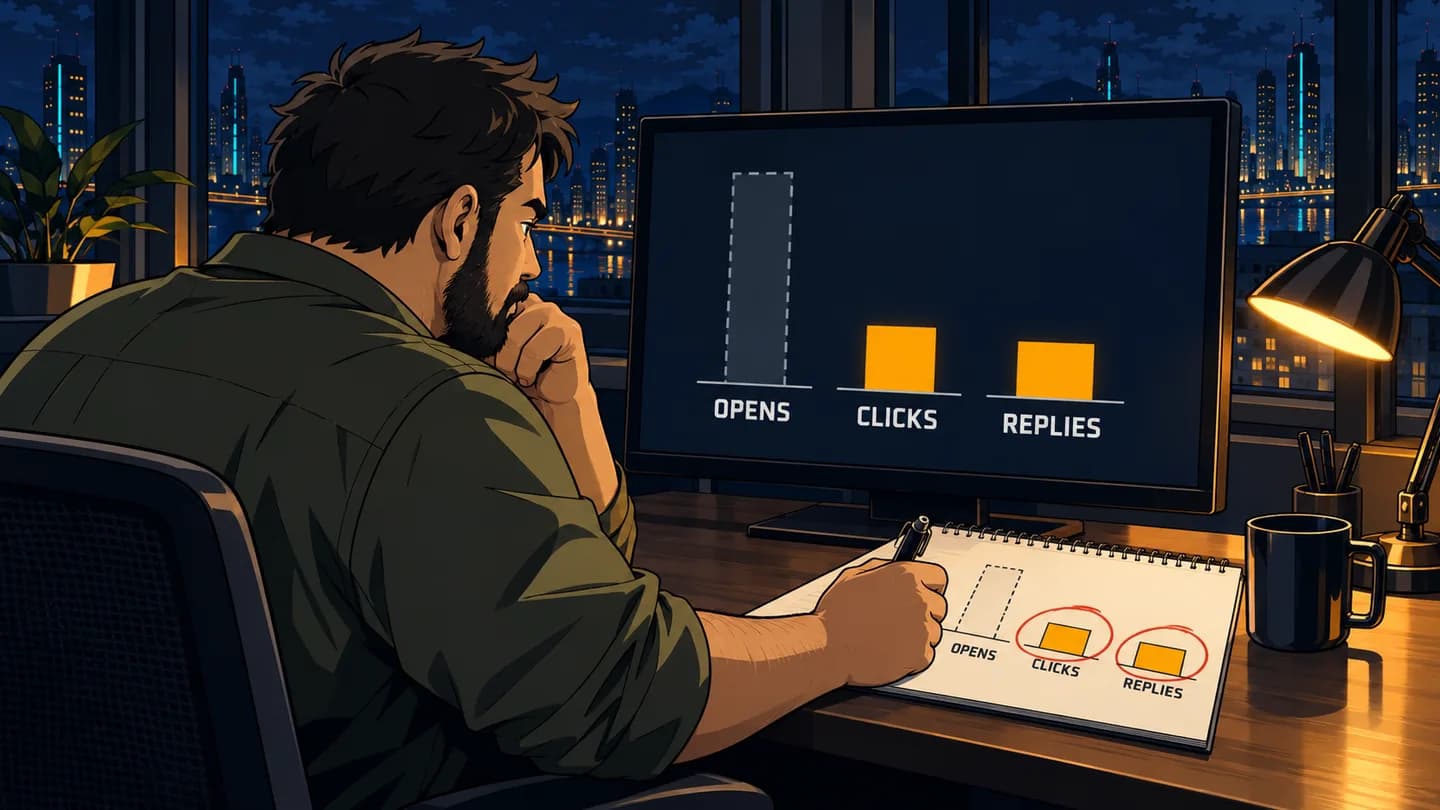
The open count appears larger, but privacy protection makes it an unreliable reading signal. Clicks and replies are smaller observable actions to investigate.
Bad result: A rising open rate with flat clicks and replies does not establish that more people are reading. Mailchimp's published averages were 35.63% opens and 2.62% clicks for campaigns with at least 1,000 subscribers, using data as of December 2023; Mailchimp also cautions that Apple's privacy changes affect open-rate accuracy. Use those figures as context, not a target, and investigate changes in your own delivered-message and conversion counts.
Start with the three public DNS checks today, substituting your domain and DKIM selector:
dig +short TXT example.com
dig +short CNAME s1._domainkey.example.com
dig +short TXT _dmarc.example.com

Put your next steps in order
Build on what you have just read with a free ebook on semantic SEO and AI visibility. Get worked examples, decision rules, checklists and a do-this-week action in every chapter, plus a six-week plan for your site.